> For the complete documentation index, see [llms.txt](https://docs.material.security/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://docs.material.security/whats-new/previous-releases/version-1.63.md).
# Version 1.63
Version 1.63 gives you a clearer picture of what's at risk and more control over what you do about it. A rebuilt Email Identity Protection report shows how identity-threat messages were actually handled, a new Blast radius card puts an OAuth app's data exposure on its detail view, and file issues let you configure and start a response without touching the detection's shared policy.
This release also brings expiration dates to API tokens, connection errors onto the integrations list, and the detection editor to sensitive categories.
***
## :tada: New
### A rebuilt Email Identity Protection report
To see the report, from the left navigation expand **Reports**, expand **Identity Threats**, then click **Email Identity Protection**. The report has been rebuilt end to end, so the numbers reconcile and every message lands in exactly one outcome.
Each message now falls into one of three handling outcomes, with no overlap between them:
* **Delivered without verification**
* **Held before delivery**
* **Blocked**
For the messages Material held, a second breakdown shows what happened next: whether the recipient **Retrieved** the message, **Reported as unrequested**, hit a **Verification failed**, made **No verification attempt**, or still has **Verification outstanding**. That tells you whether holds are being resolved or piling up.
The report also breaks activity down by message type, so you can see password resets, verification codes, account activations, and account access messages separately. A service matrix shows how each service is configured, whether that's **Protect**, **Block**, **Detect Only**, or **Disabled**, and a message access summary rounds out the picture. You can also export the report to PDF.
{% hint style="info" %}
The Email Identity Protection report is available for customers with [Account Takeover Resilience](https://docs.material.security/getting-started/fundamentals/account-takeover-resilience) (ATOR) licenses.
{% endhint %}
***
### See an OAuth app's blast radius
Open an OAuth app from **Explorer** > **Apps** > **OAuth Apps** and the detail view now carries a **Blast radius** card: how much sensitive content the app's connected accounts can reach, counted across files and messages.
Each count links straight through to those files or messages in Explorer, so you can go from "this app is risky" to "here's exactly what it can see" without leaving the app.
The card only shows what genuinely applies to the app in front of you:
* An app with no access to mail or files doesn't get a card at all
* An app that can reach only one of the two shows only that count
* A files count doesn't appear if your tenant isn't syncing Drive content
The **View all** links behind these counts now return the full set of accounts rather than stopping short, so the list you open matches the number you clicked.
{% hint style="info" %}
Learn more about [investigating malicious OAuth apps](https://docs.material.security/learn-more/risk-areas/malicious-oauth-apps/).
{% endhint %}
***
### Move messages back to the inbox through the API
A new `POST /api/v1/messages/move-to-inbox` endpoint returns messages to the inbox, up to 200 message IDs per call. Material queues the work across every mailbox holding a copy, so a message that went to several people comes back for all of them. Any IDs Material can't resolve come back in a `notFound` list, so a partial batch tells you which ones to look at.
This gives you a programmatic path to undo a quarantine or a misfiled batch, rather than working through the messages by hand.
{% hint style="info" %}
Learn more about the [v1 API](https://docs.material.security/reference/api-v1).
{% endhint %}
***
## ✨ Enhancements
### File Security
#### Configure and start a response from a file issue
The **Response** section on a file issue is now editable in place. Choose the remediation actions you want, whether that's an email notification, a permissions update, a label change, or a grace period, then save. Material runs them against that one file straight away and records what it started at the bottom of the issue detail view.
The detection's shared default policy stays exactly as it was. Previously a file issue pointed you at the detection to change anything, which meant a one-off fix rewrote the policy for every file the detection covers.
A few related accuracy fixes come with it:
* Completion checkmarks show on the steps that actually ran, and stay off the ones you've just added or reconfigured
* A grace period you add lands at the end of the step list, and a grace period with nothing after it no longer blocks saving
* When a detection's grace period is extended while an issue is already waiting, the step shows the configured duration instead of a date that has gone stale
{% hint style="info" %}
Learn more about [configuring default responses](https://docs.material.security/getting-started/fundamentals/respond/configure-default-responses).
{% endhint %}
#### Change a file's permissions from its detail page
A file's detail page now lets you change who can reach it without going to Drive. You can change an existing person's or group's access level, remove a permission, or add a new one. Accounts enrolled in your tenant are searchable, and you can type an external address directly.
Material checks your Workspace sharing policy before applying the change and tells you when the policy won't allow it, rather than appearing to succeed and silently doing nothing.
**Revoke external access** is unchanged, so the one-click path for fast triage is still there.
{% hint style="info" %}
Learn more about [remediating and revoking access to files](https://docs.material.security/learn-more/risk-areas/file-data-security/bulk-remediate-and-revoke-access-to-files).
{% endhint %}
#### **Drive detections honor your Workspace sharing policies**
Google Workspace lets you turn off external or link sharing for an organizational unit. When you do, Google stops the links working but leaves them on the file, so Material flagged those files as publicly shared even though nobody outside your organization could open them.
Material now reads your Google Workspace organizational unit and group Drive sharing policies. For each file, it determines the effective policy the same way Google Workspace does, then uses it when evaluating your file detections:
* **My Drive**: the file owner's organizational unit policy
* **Shared drive**: the policy of the organizational unit the shared drive belongs to
Groups can override organizational unit policies, and Material applies the group policy when one exists. A file your policies keep login-restricted is no longer flagged as publicly shared, so your file issues reflect real exposure. The file's detail page shows the policy that applied, so you can see why a file was or wasn't flagged.
When you change a sharing policy in Workspace, Material updates the files it affects and opens or closes issues to match. This can take a day or two to fully reflect.
{% hint style="warning" %}
Material applies your sharing policies only after you grant a read-only sharing-policy permission. To grant it, click **Action Required: Grant additional permissions** in the bottom left, then click **Review permissions** and follow the prompts. Until you grant it, your file detections behave as they do today. New customers grant this permission during onboarding.
{% endhint %}
{% hint style="info" %}
Learn more about [Google Workspace sharing policies](https://docs.material.security/learn-more/risk-areas/file-data-security/google-workspace-sharing-policies).
{% endhint %}
***
### OAuth apps and accounts
#### Suggested classifications arrive as a draft
When Material suggests a classification for an OAuth app, the **Classification** and **Response** cards now open already filled in and highlighted, with an unsaved-changes indicator. You review what's proposed and save it, or change it first.
{% hint style="info" %}
Learn more about [OAuth detections and classification](https://docs.material.security/learn-more/risk-areas/malicious-oauth-apps/oauth-detections-and-classification).
{% endhint %}
#### Tenant column on the global email apps view
In **Explorer** > **Apps** > **Email**, the **Tenant** column is shown by default when you're in the Global view. The same app can appear once per tenant, and now the rows say which tenant each one belongs to.
***
### Detections
#### Sensitive categories get the detection editor
Creating and editing a custom sensitive category now uses the same full-page editor as custom detections. To get there, from the left navigation expand **Detections**, then click **Sensitive Categories**.
You get the editor's full set of tools:
* A name and description filled in for you from the criteria you've written
* A live preview of what the category would match
* **⌘K** to save, and a prompt if you try to leave with unsaved changes
* Severity and email response in the sidebar, saved together with the rest
{% hint style="info" %}
Learn more about [sensitive categories](https://docs.material.security/learn-more/risk-areas/email-data-security/sensitive-categories).
{% endhint %}
#### **Google data export alerts no longer imply a full export**
When a Workspace super admin runs a Data Export (Takeout) from the Google Admin console, Google raises an alert and labels it "domain-wide takeout," even when the export covered a handful of selected users. Material's detection followed that naming, so every one of these issues read as though someone had exported your entire organization.
The detection is now **Google admin started a Workspace data export**, and the evidence on the issue is titled **Admin Data Export (Takeout)**. The description is honest about what the alert does and doesn't carry: you get the admin who started the export and a request ID, and neither one tells you the scope. To see what was actually exported, check the [Data Export tool](https://knowledge.workspace.google.com/admin/migrate/export-all-your-organizations-data) in the Google Admin console.
***
### Platform and administration
#### Set an expiration when you create an API token
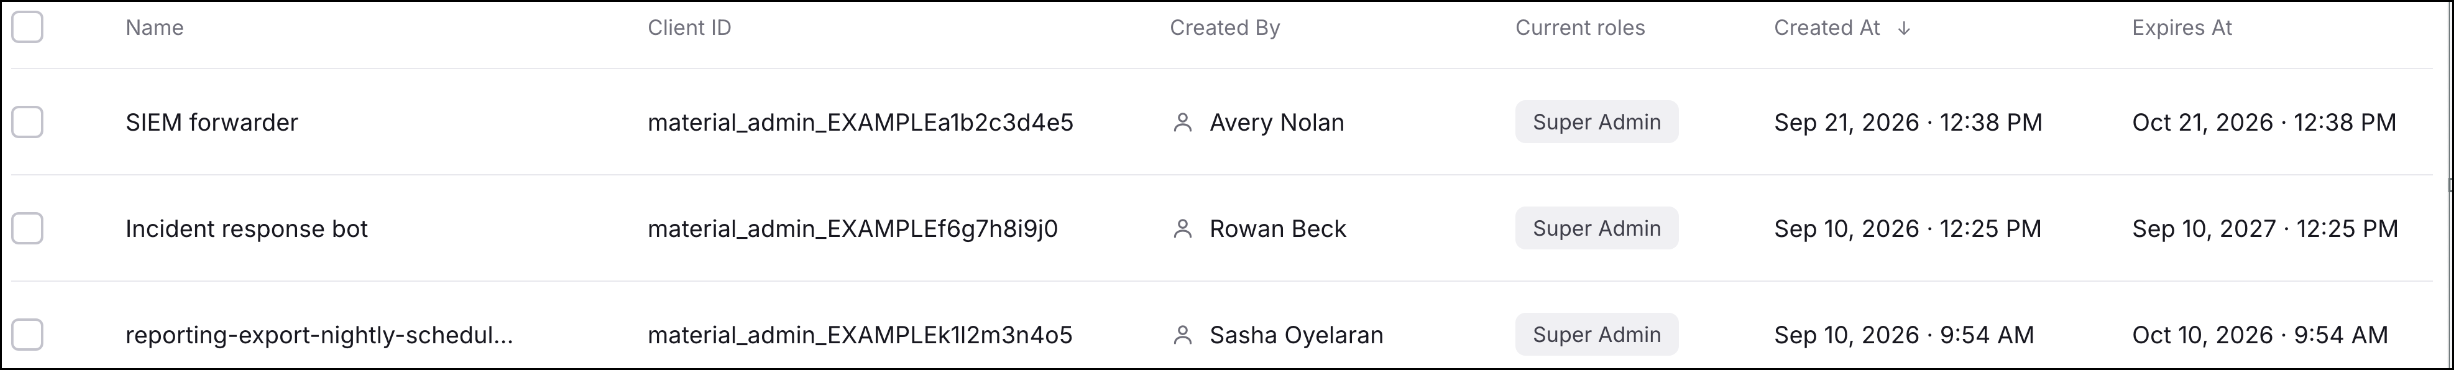
API tokens now have expiration dates. Choose a duration them when you create them, or edit existing API tokens to set a shorter expiration date than what is already there.
Short-lived credentials are easier to justify than permanent ones, and the list now tells you which tokens are on a clock.
Learn more about [authenticating to the v1 API](https://docs.material.security/reference/api-v1/authentication).
#### See when an integration's connection is failing
A failing integration now says so in the product. A warning badge appears next to the integration in the list, and opening it shows a callout with the error Material last received.
Previously a connection could stop working quietly, and you'd find out when the data stopped arriving somewhere else.
{% hint style="info" %}
Learn more about [integration fundamentals](https://docs.material.security/integrations/integration-fundamentals).
{% endhint %}
#### SAML sign-in works with more identity providers
A SAML integration can now request a specific NameID format instead of always asking for an email address. If your identity provider is keyed on something other than email, such as a user principal name, sign-in that starts from Material now completes rather than stopping on an error.
Your Material team sets the format on your integration, so get in touch if your provider needs one.
{% hint style="info" %}
Learn more about [Admin SSO](https://docs.material.security/learn-more/administration/security/admin-sso).
{% endhint %}
***
## 🐛 Fixes
**Detections and file security**
* Improves sensitive-content scanning when records contain invalid data.
* Material no longer reports that it has no history for a sender when history exists, so novel-sender signals reflect what Material actually knows.
* File and message search no longer fails when you search on the apps that can reach a file or account before that index has been built. You get a clear message explaining why instead of an error.
* Opening **Manage Inherited Permissions** on a Google Drive folder shows the folder name once, rather than repeating it several times down the page.
* In **Explorer** > **Files**, selecting all results on a large result set no longer makes the page stop responding.
* The **File issue resolution** section of the File Security report leaves out its zero-count sentences, so the summary no longer reports on files it didn't find.
**Issues and investigation**
* The **Response** section on an issue no longer says a message was blocked or protected unless Material actually took that action. Previously any message appearing in the issue's evidence was described that way, which made detection-only issues look remediated.
* The **Analysis** and **Date** columns no longer shift around while you're reading a detection-grouped issue list.
* Message details open faster. Material renders from recent data it already holds and fills in the rest behind it, rather than waiting for the full lookup before showing you anything.
* Message details for very large emails now load reliably, and the lookup is recorded in the audit log.
* In the batch actions menu, **ESC** always closes the menu and the arrow keys move through actions and back out of a group, so you can work through a batch without reaching for the mouse.
* Recommended classification now stays current on email threat issues as the issue develops, in both the v1 API and the Issue Change payload your integrations receive. Previously the field was set only on OAuth app issues and stayed empty everywhere else.
* A grace period can't be saved as the last step in a response, and you can't place two grace periods back to back, so a response always ends with an action that does something.
**Platform and administration**
* The access request log shows one row per challenge for Identity Protection, with the IP address, browser, and device that made the request. A request still waiting on the end user reads **Pending** rather than **Unknown**.
* The Material logo renders correctly in the preview of a real, non-simulation attachment stub in Outlook.
* In the quick action (**⌘K**) menu for Trusted Entities, **Treat as External** and **Don't trust messages** have clearer icons, and the external and internal options carry a one-line description of what each one does.
***
## :books: New and Updated Documentation
**Updated**
* [Material MCP Server](https://docs.material.security/reference/material-mcp-server) and [Hello World](https://docs.material.security/reference/api-v1/hello-world): Adds guidance for connecting when your AI client's organization hasn't enabled custom connectors, including what to ask for and the interim path, marks OAuth as the recommended way to connect, and tightens the worked v1 API examples.
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://docs.material.security/whats-new/previous-releases/version-1.63.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.