

Version 1.29
Sender Search in Email Threat Issues
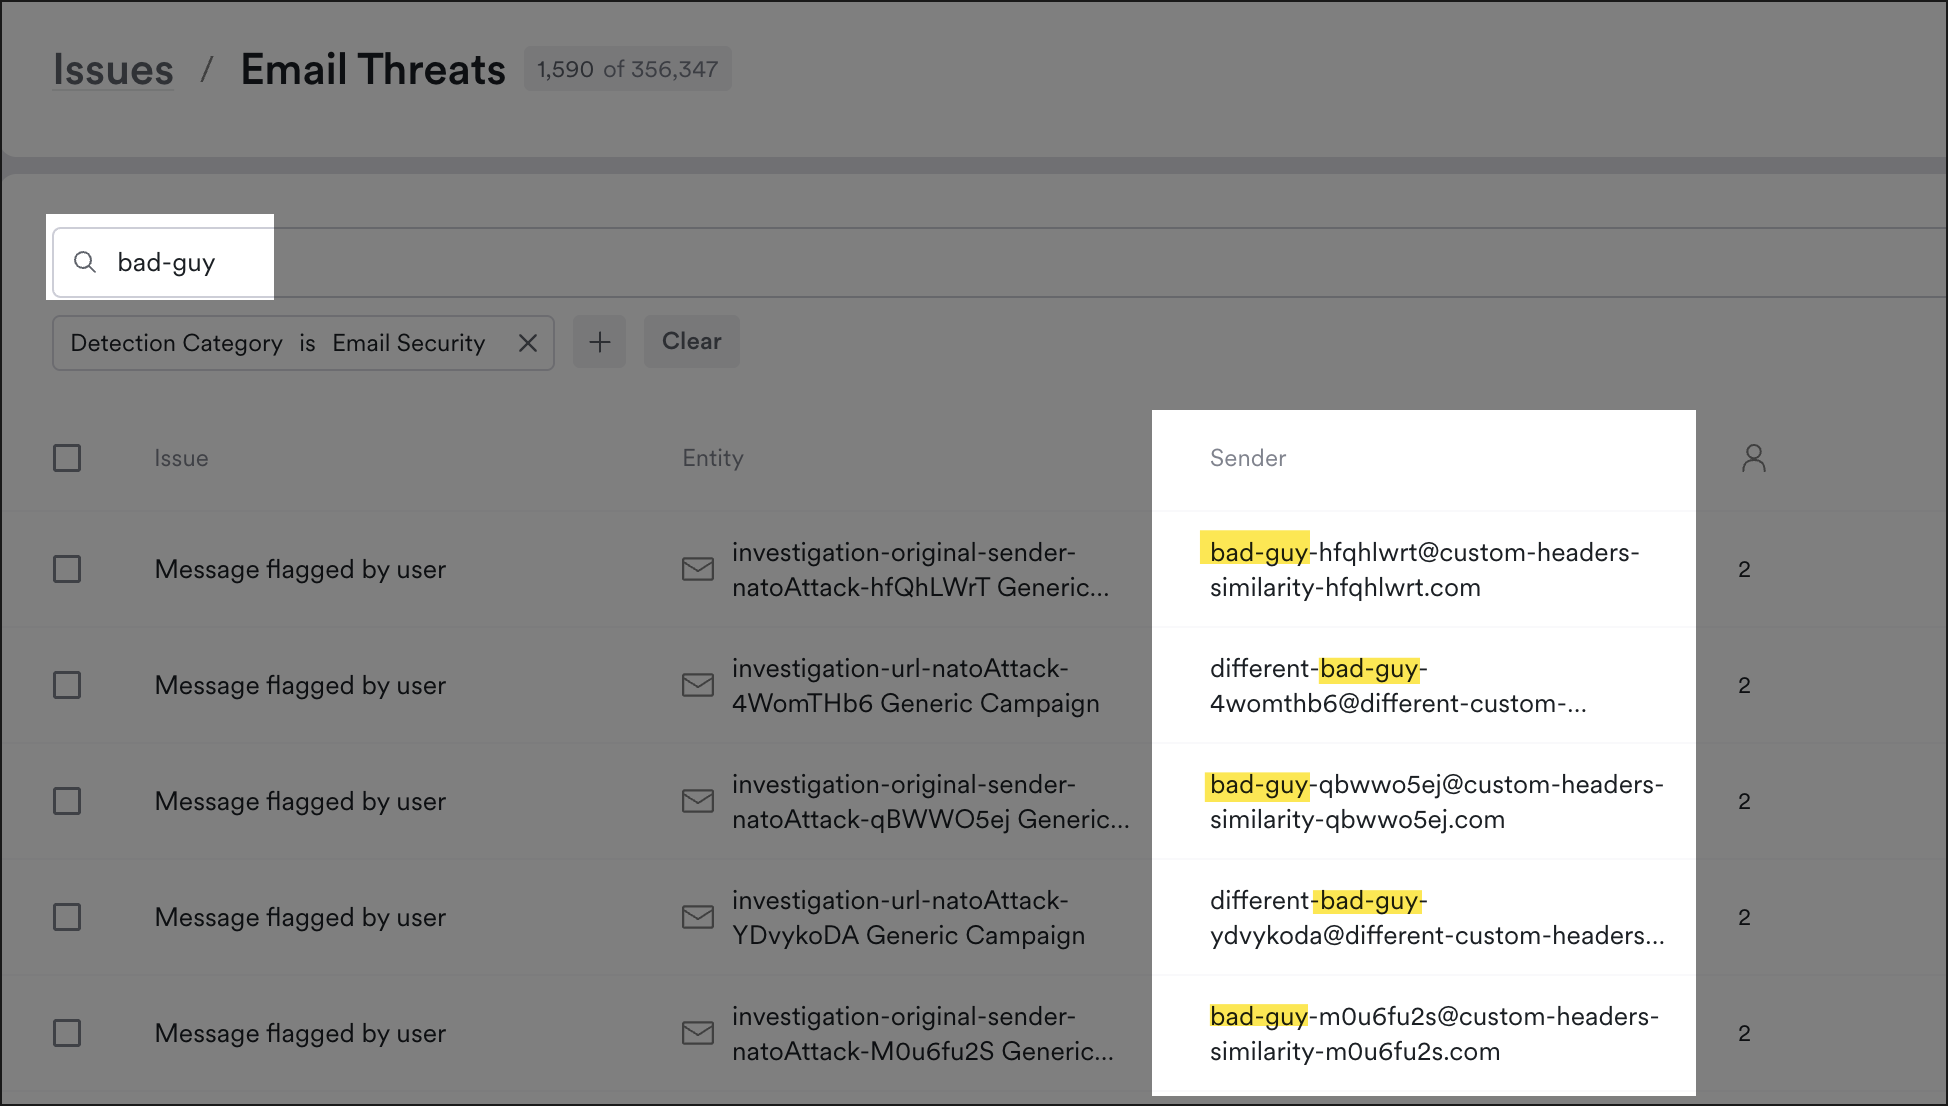
You can now search Email Threat Issues by sender. From the left navigation, expand Issues then click Email Threats.
Enter a sender name into the search field:
Issue Tab Headers
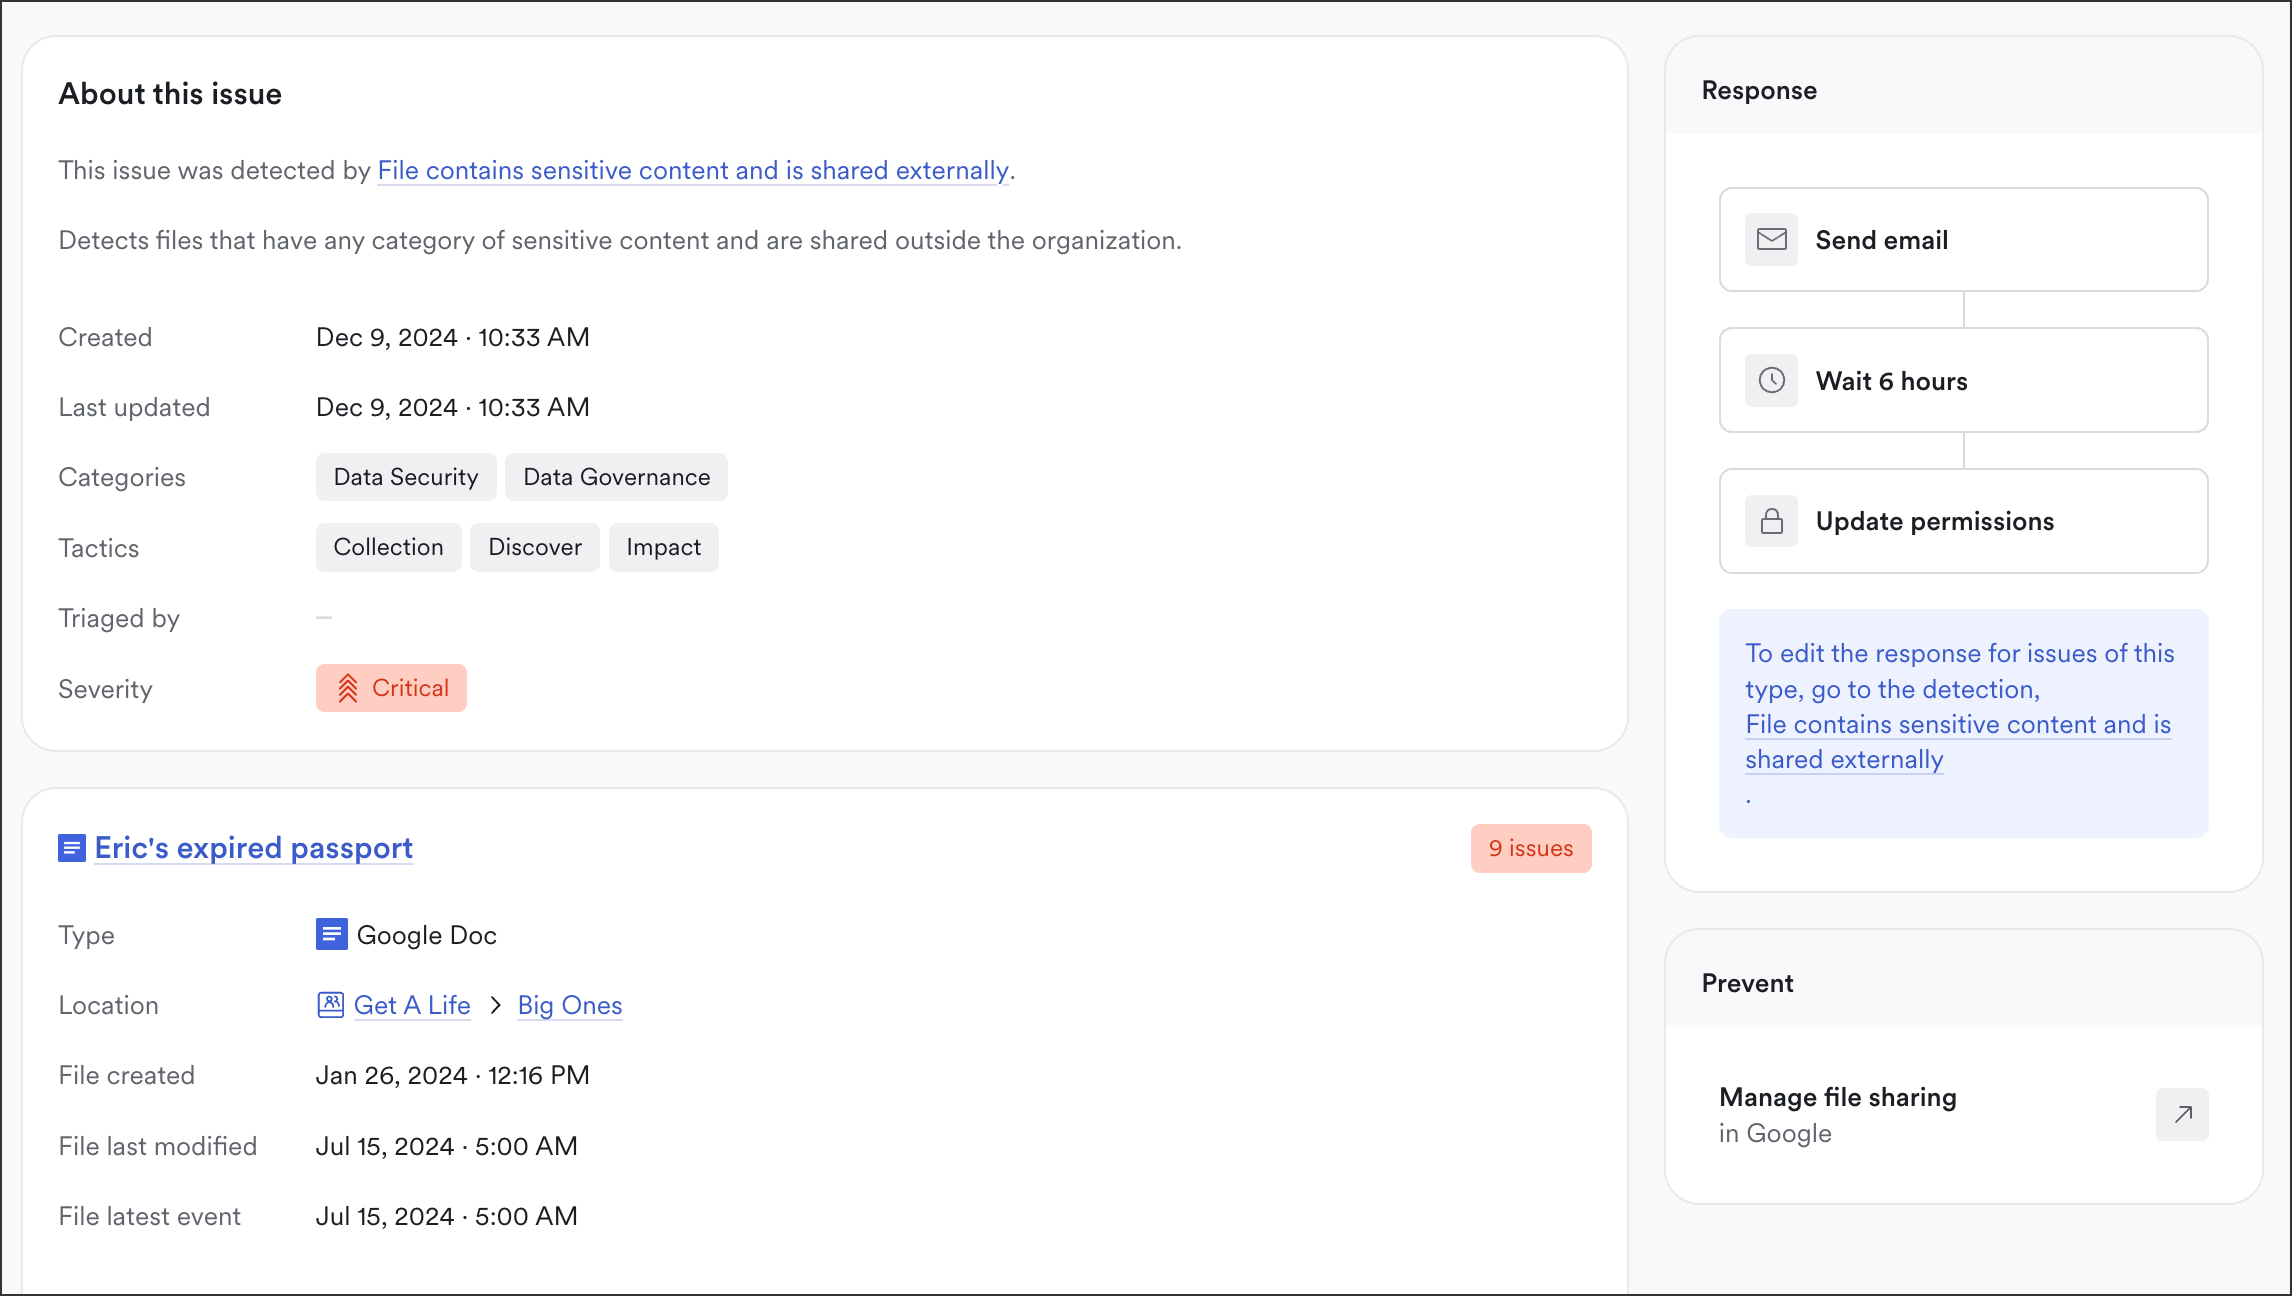
Tab headers on issues now look sharper than ever:
Create Phishing Simulations from the Real Thing
You can now create phishing simulations directly from an Email Threat issue:
From the left navigation, expand Issues then click Email Threats.
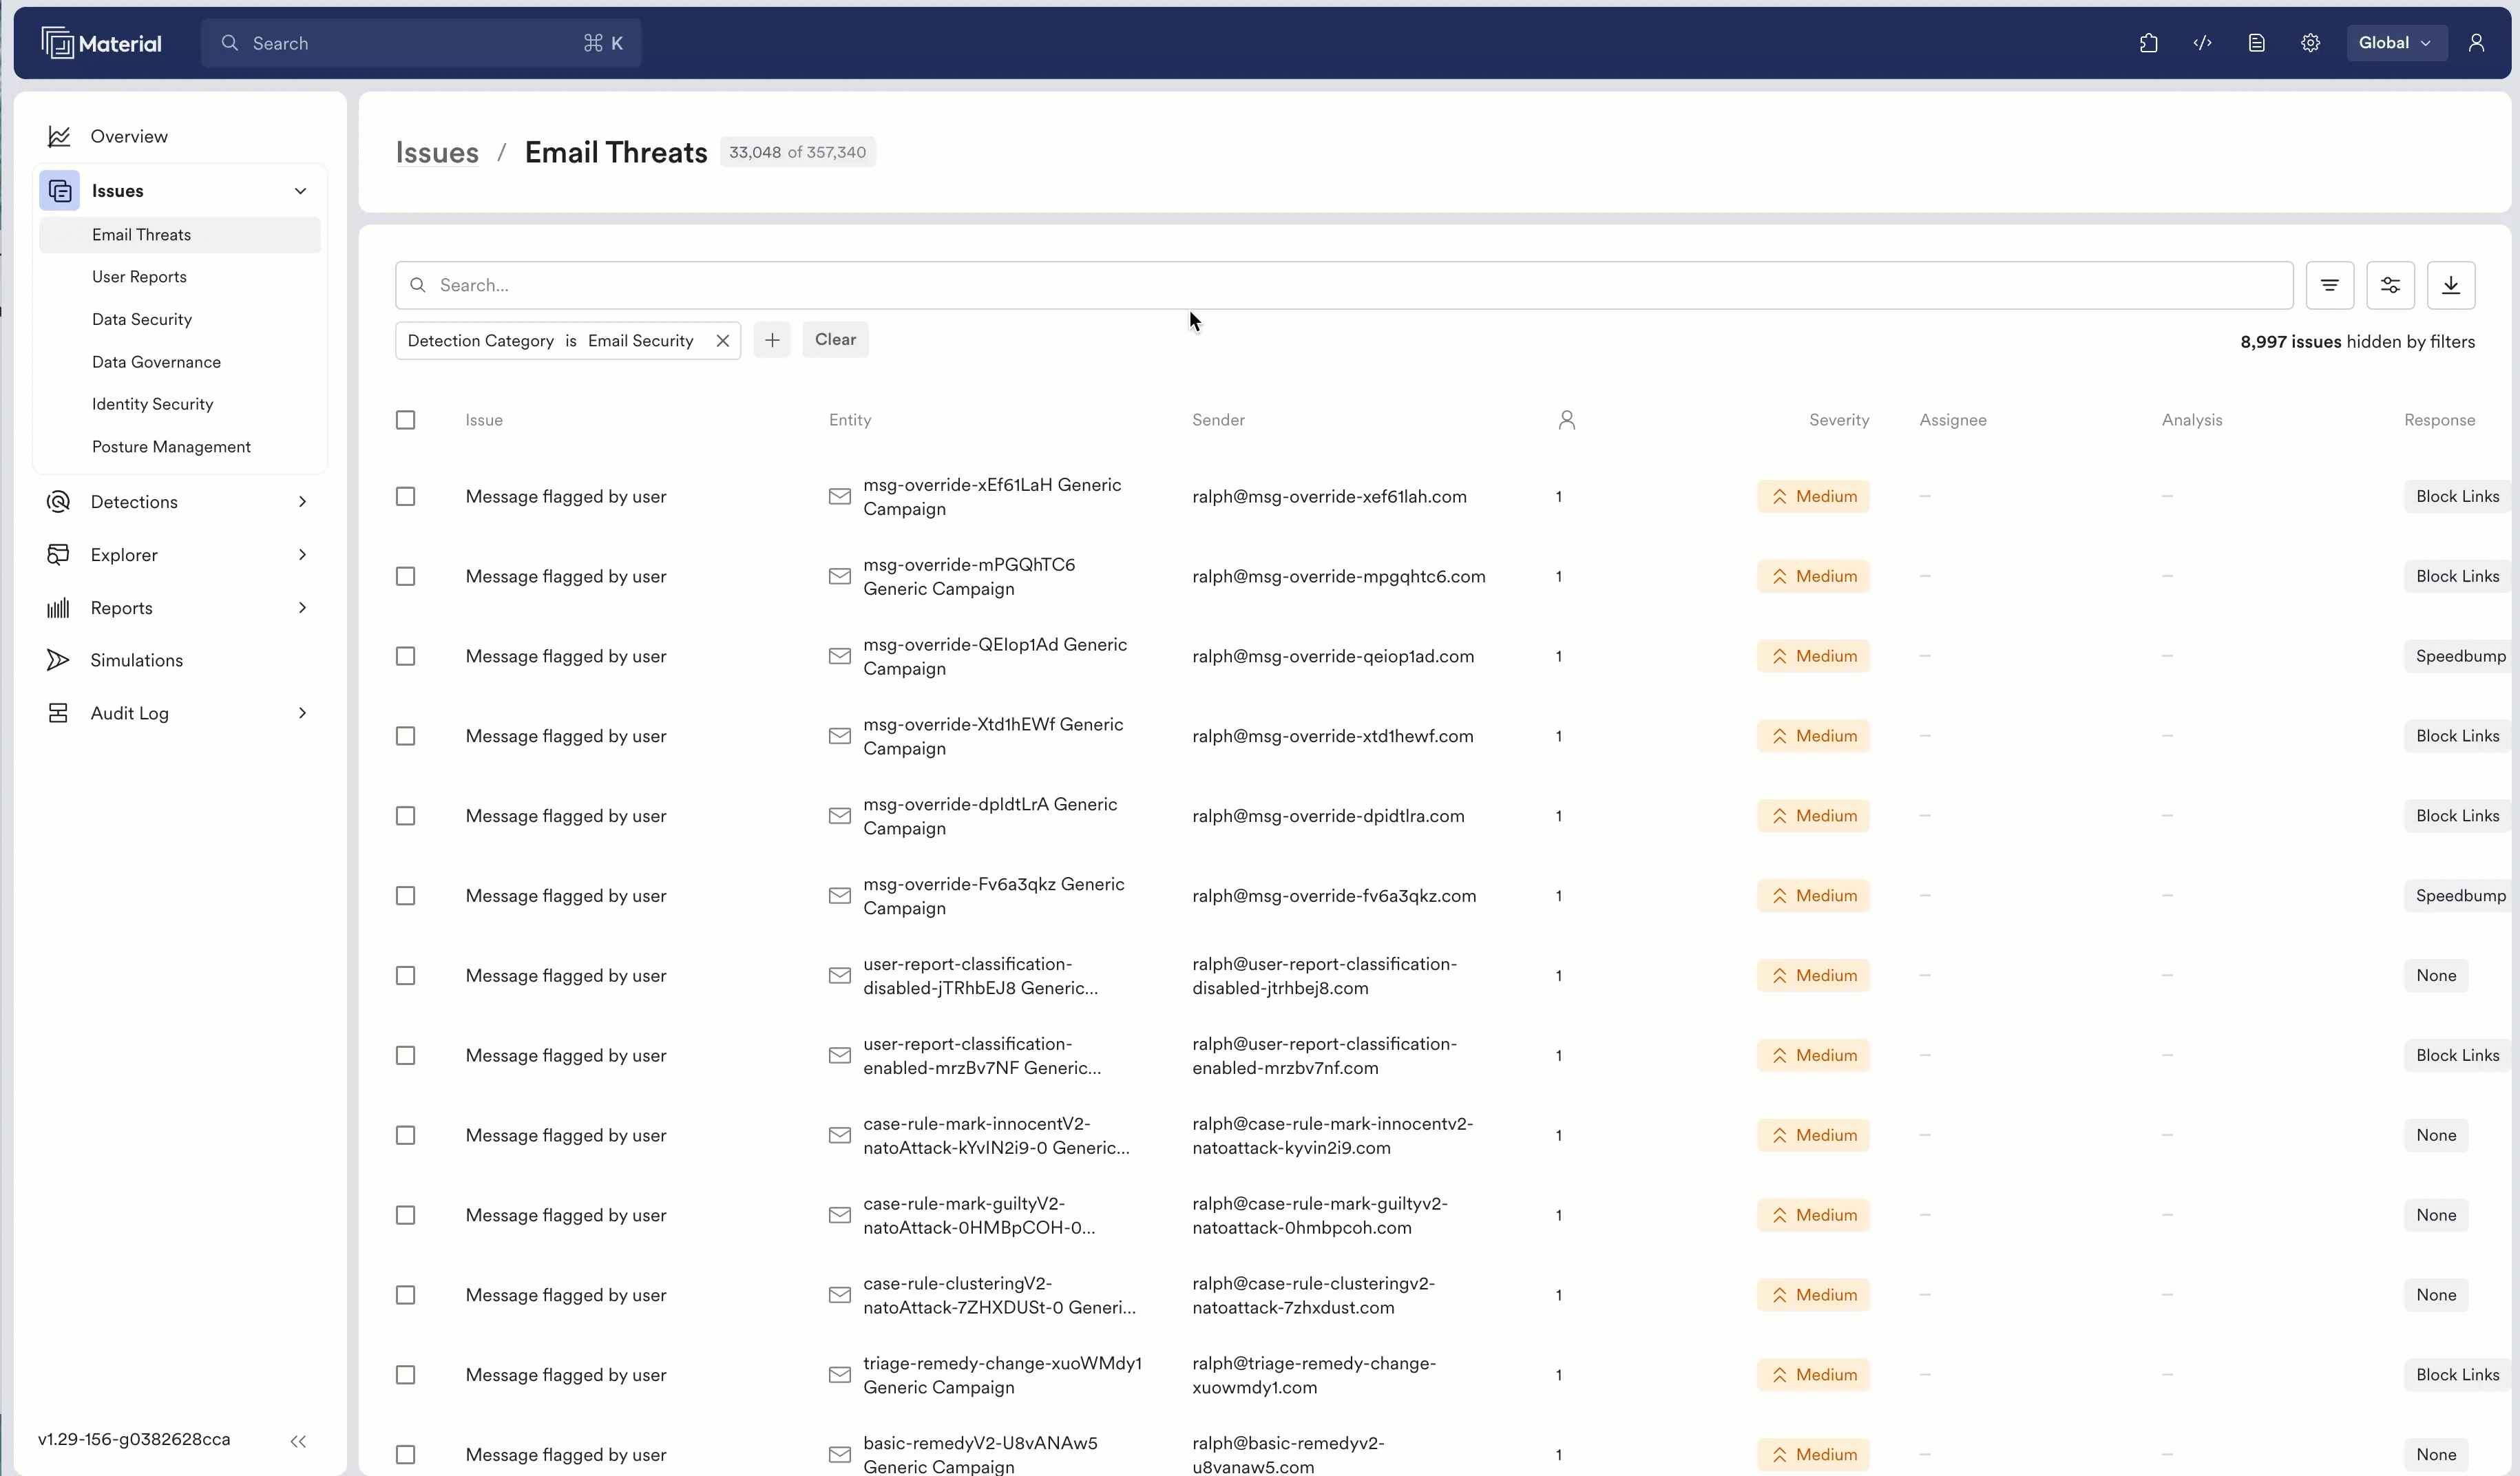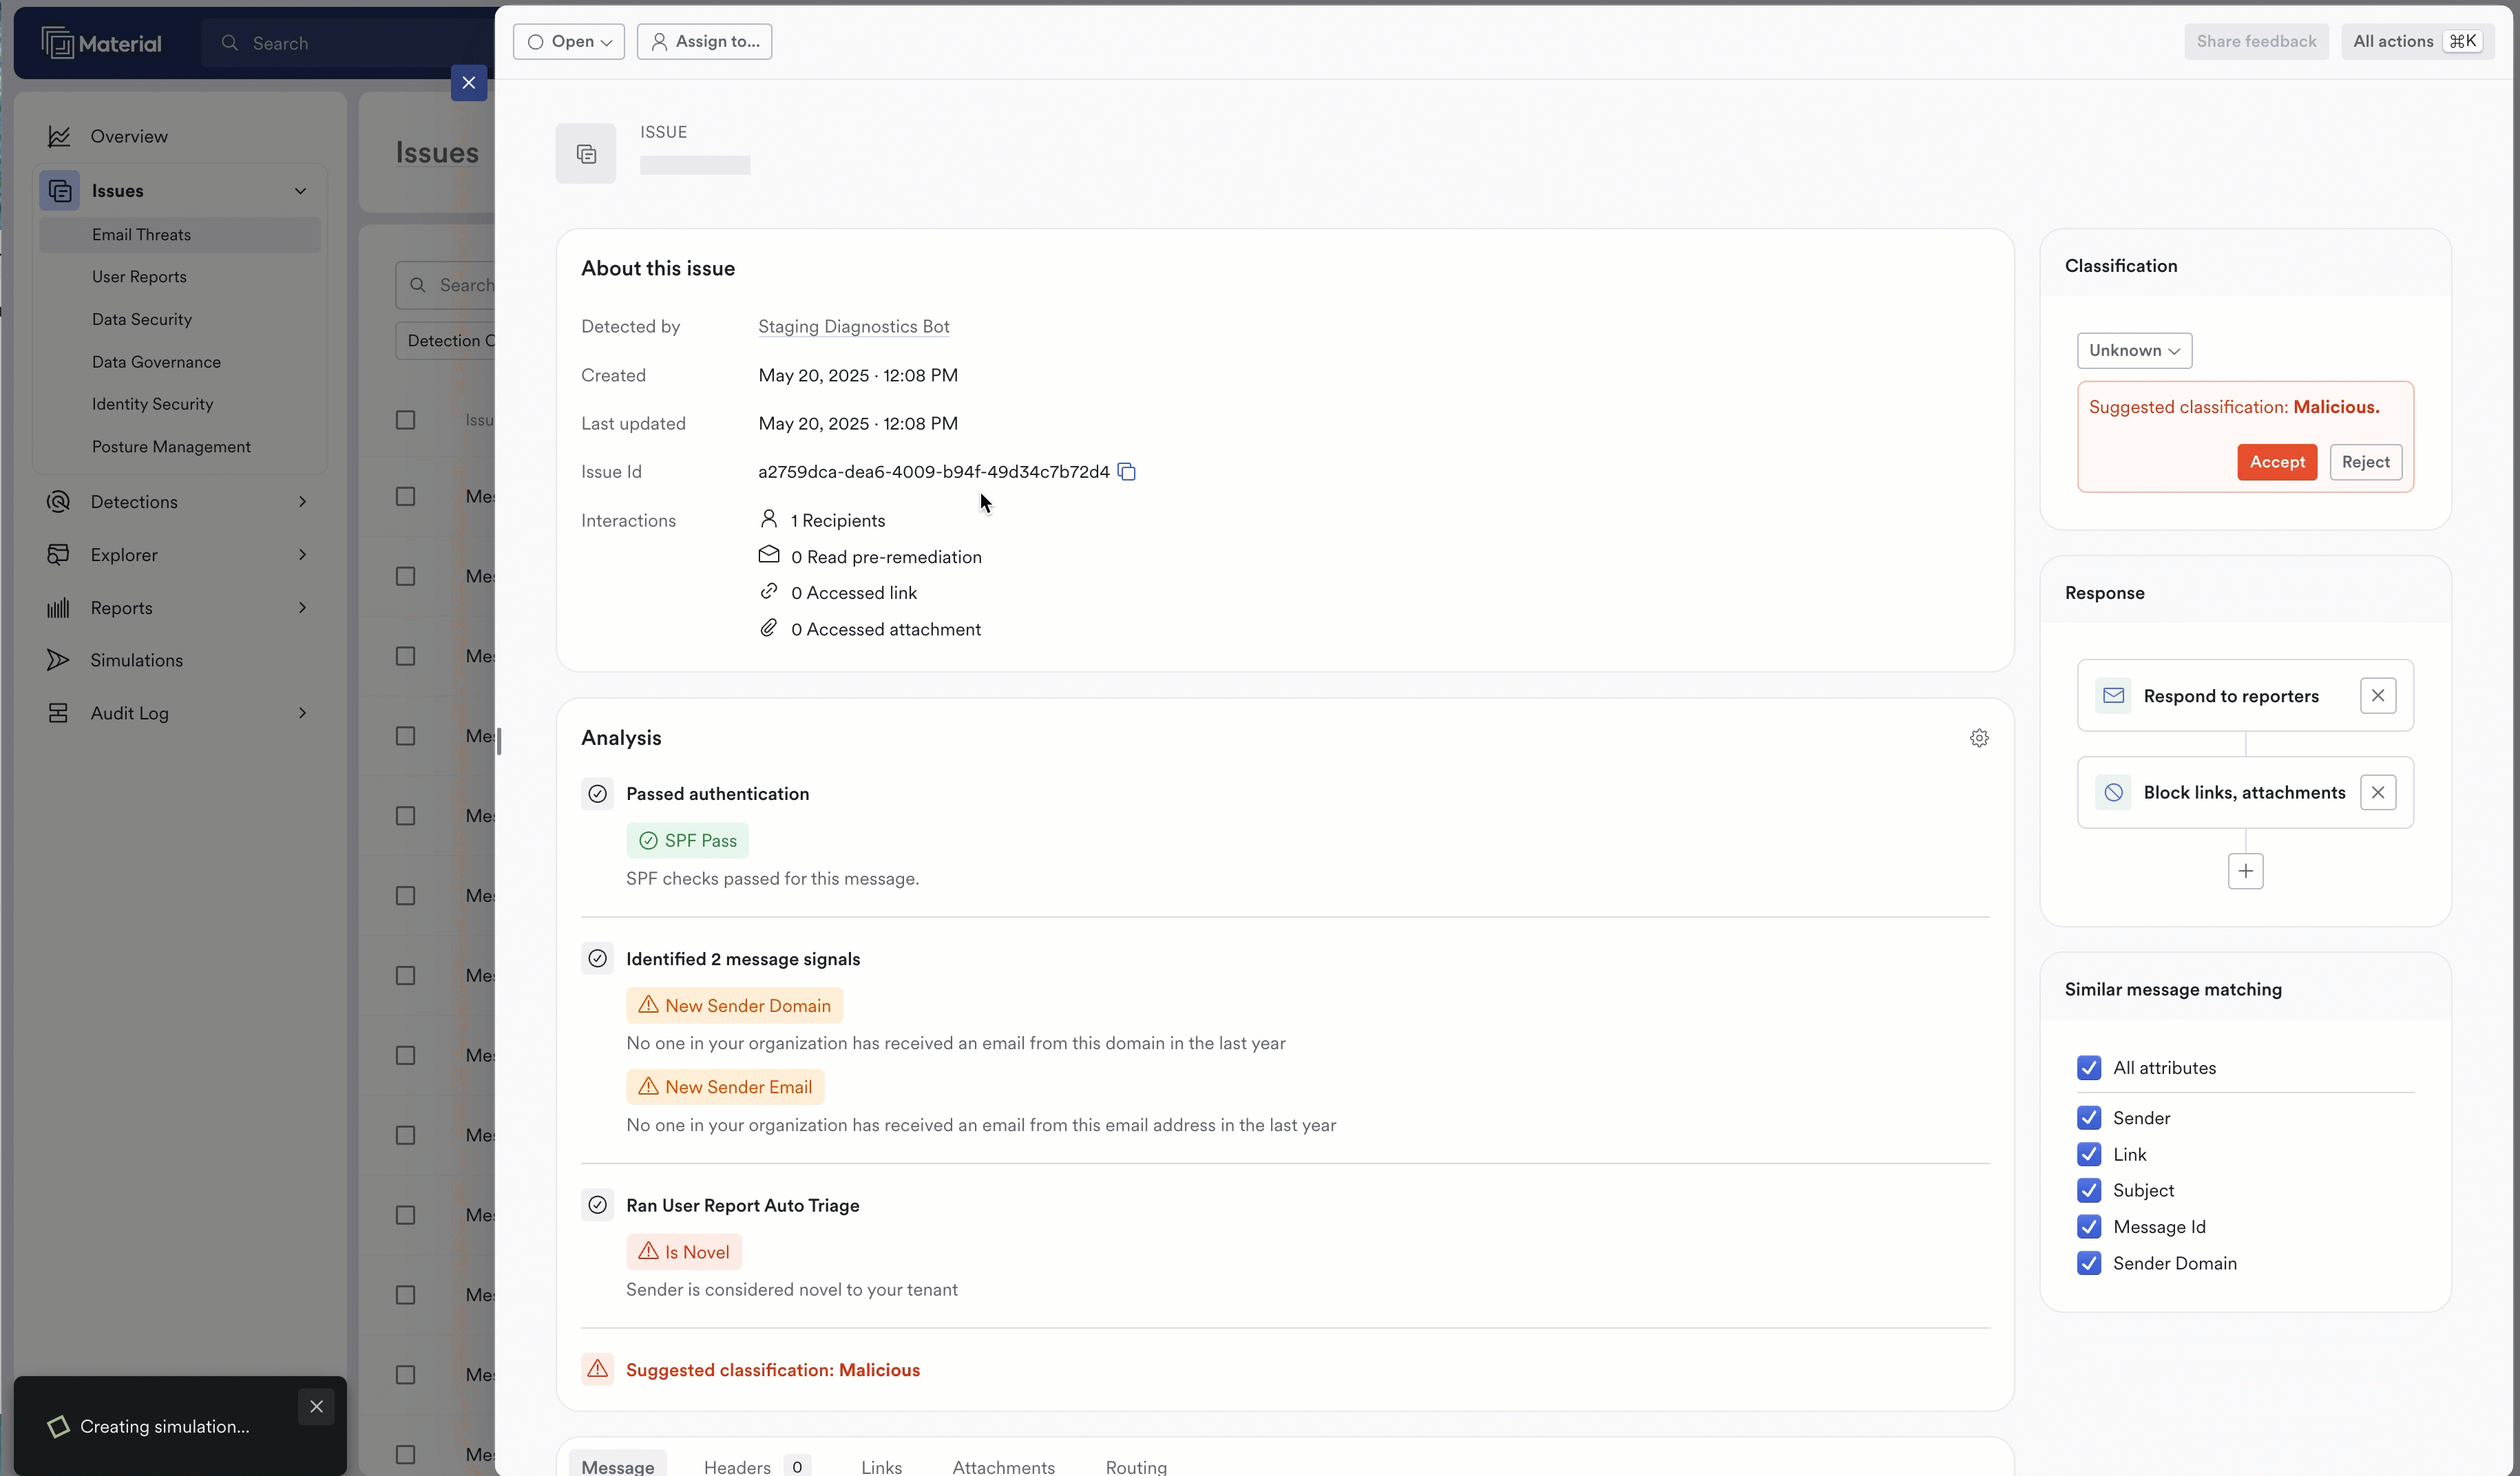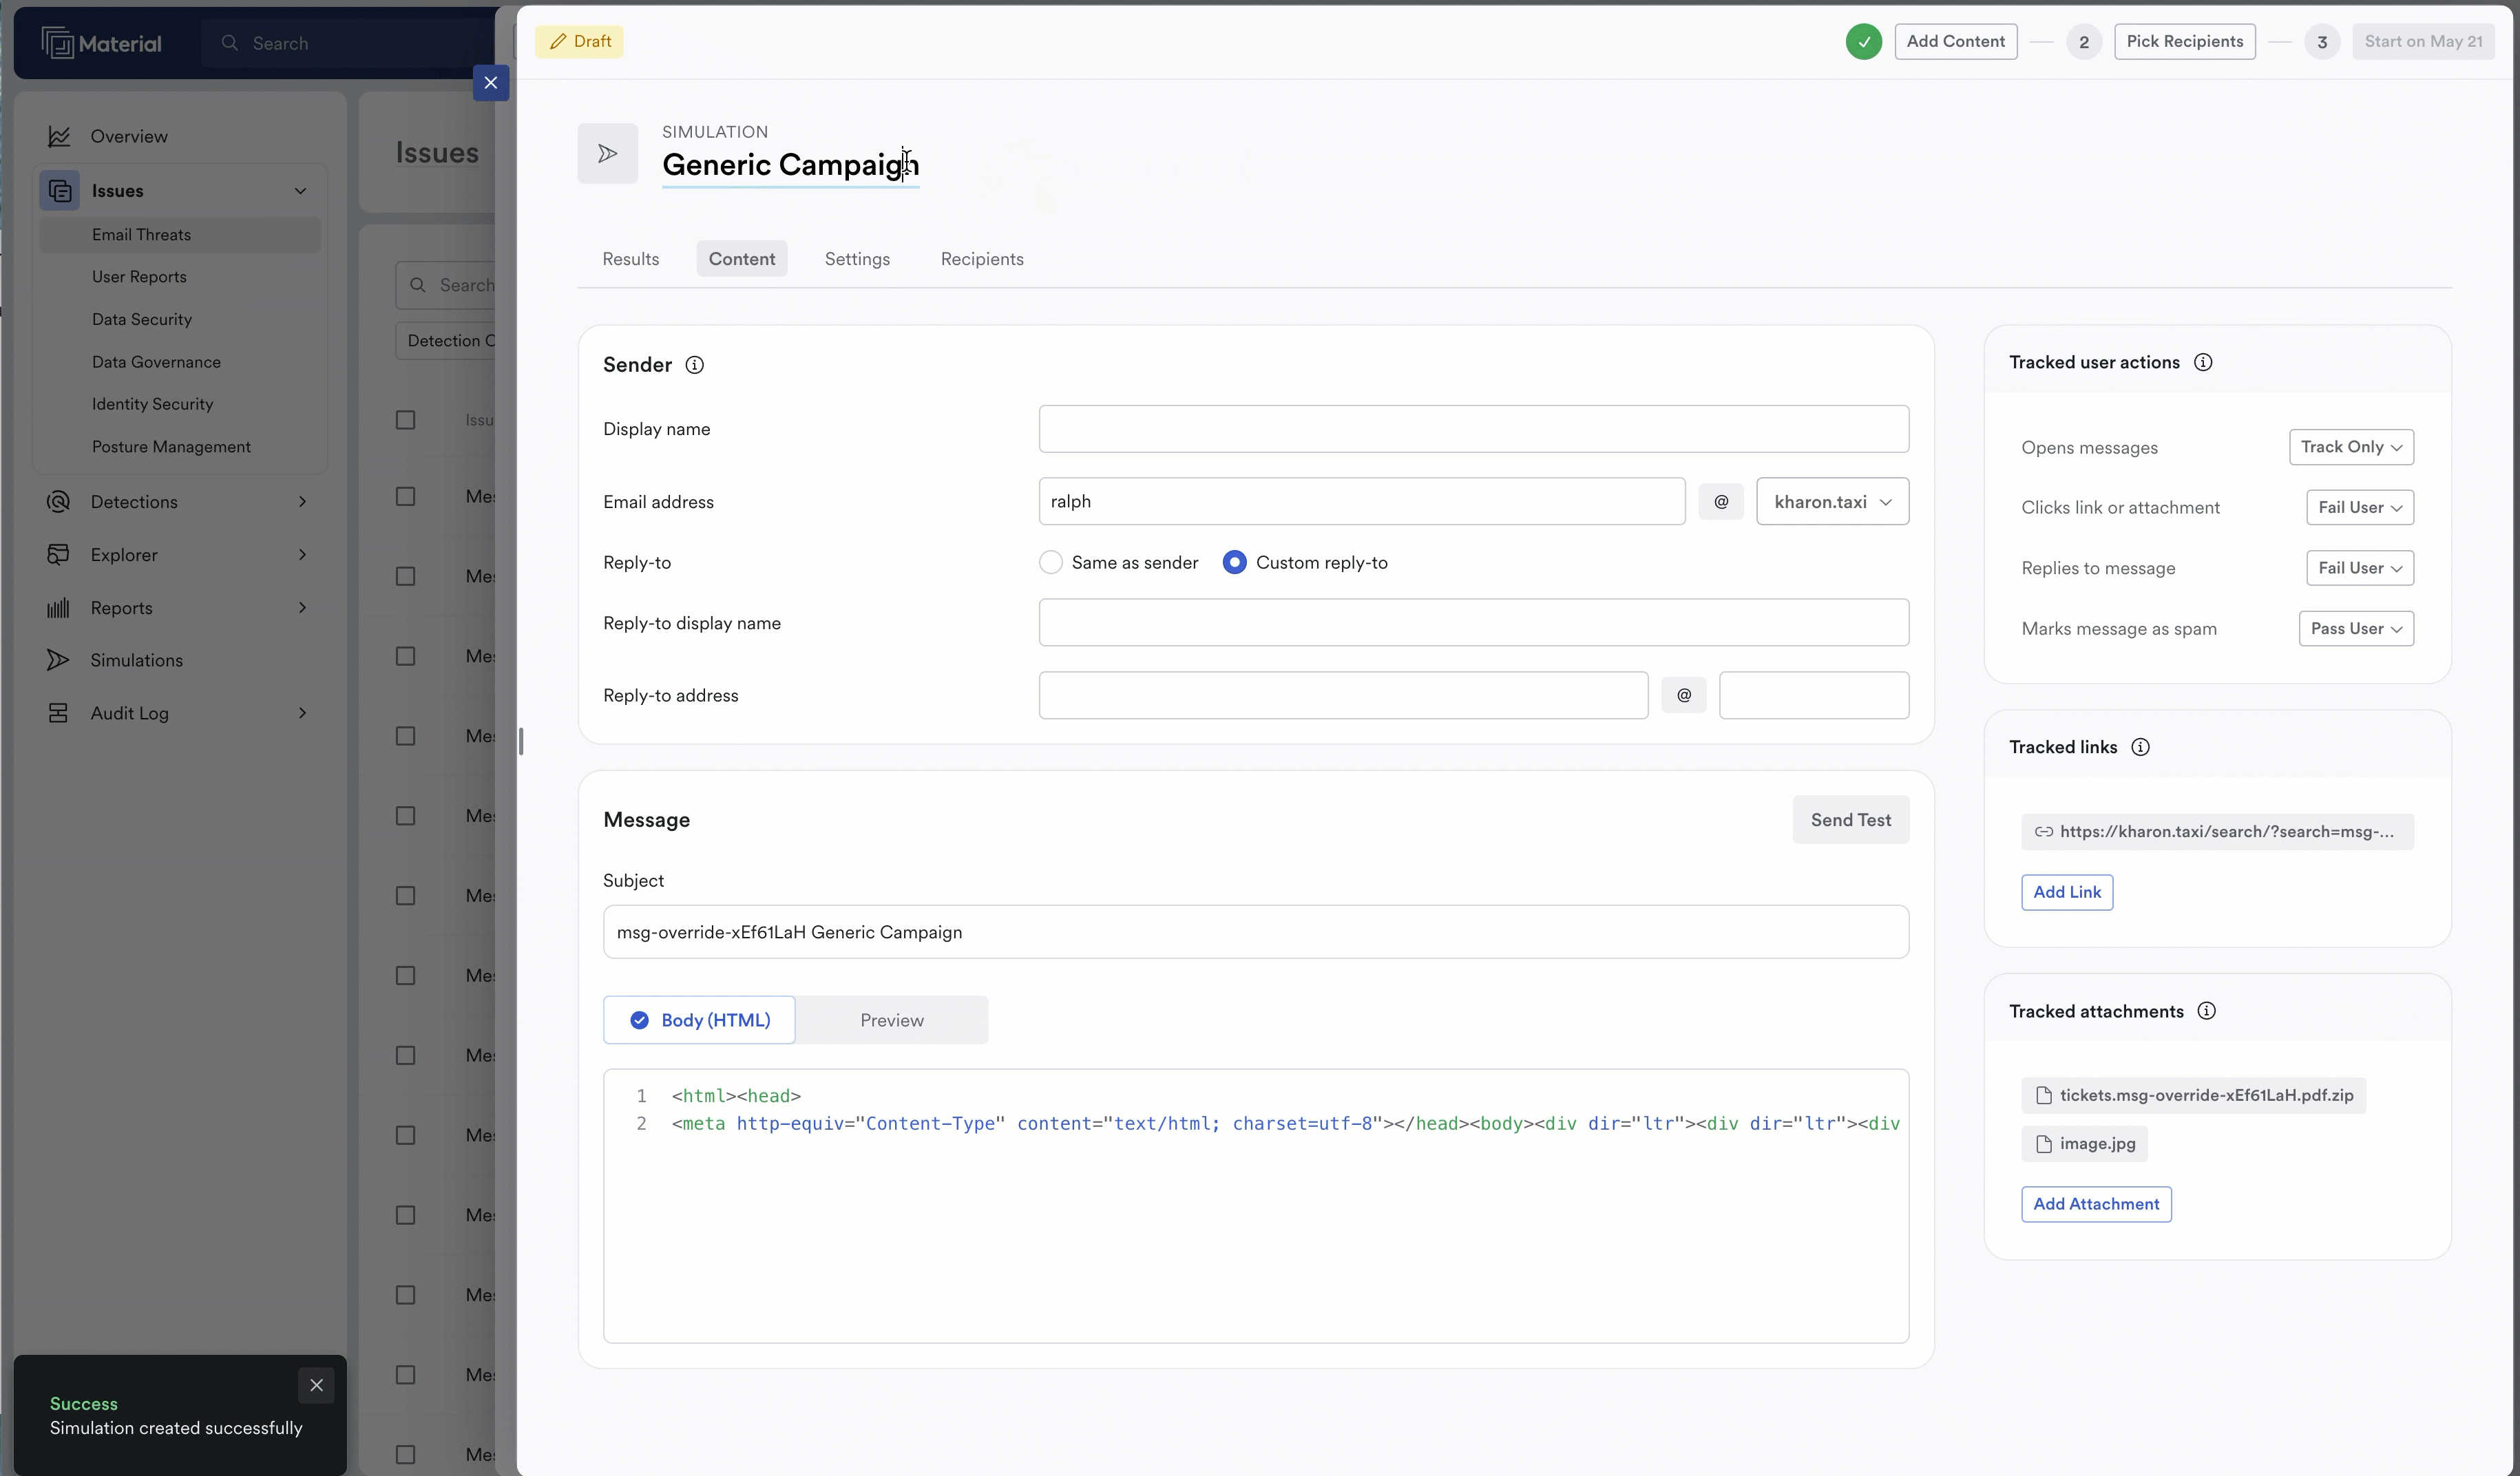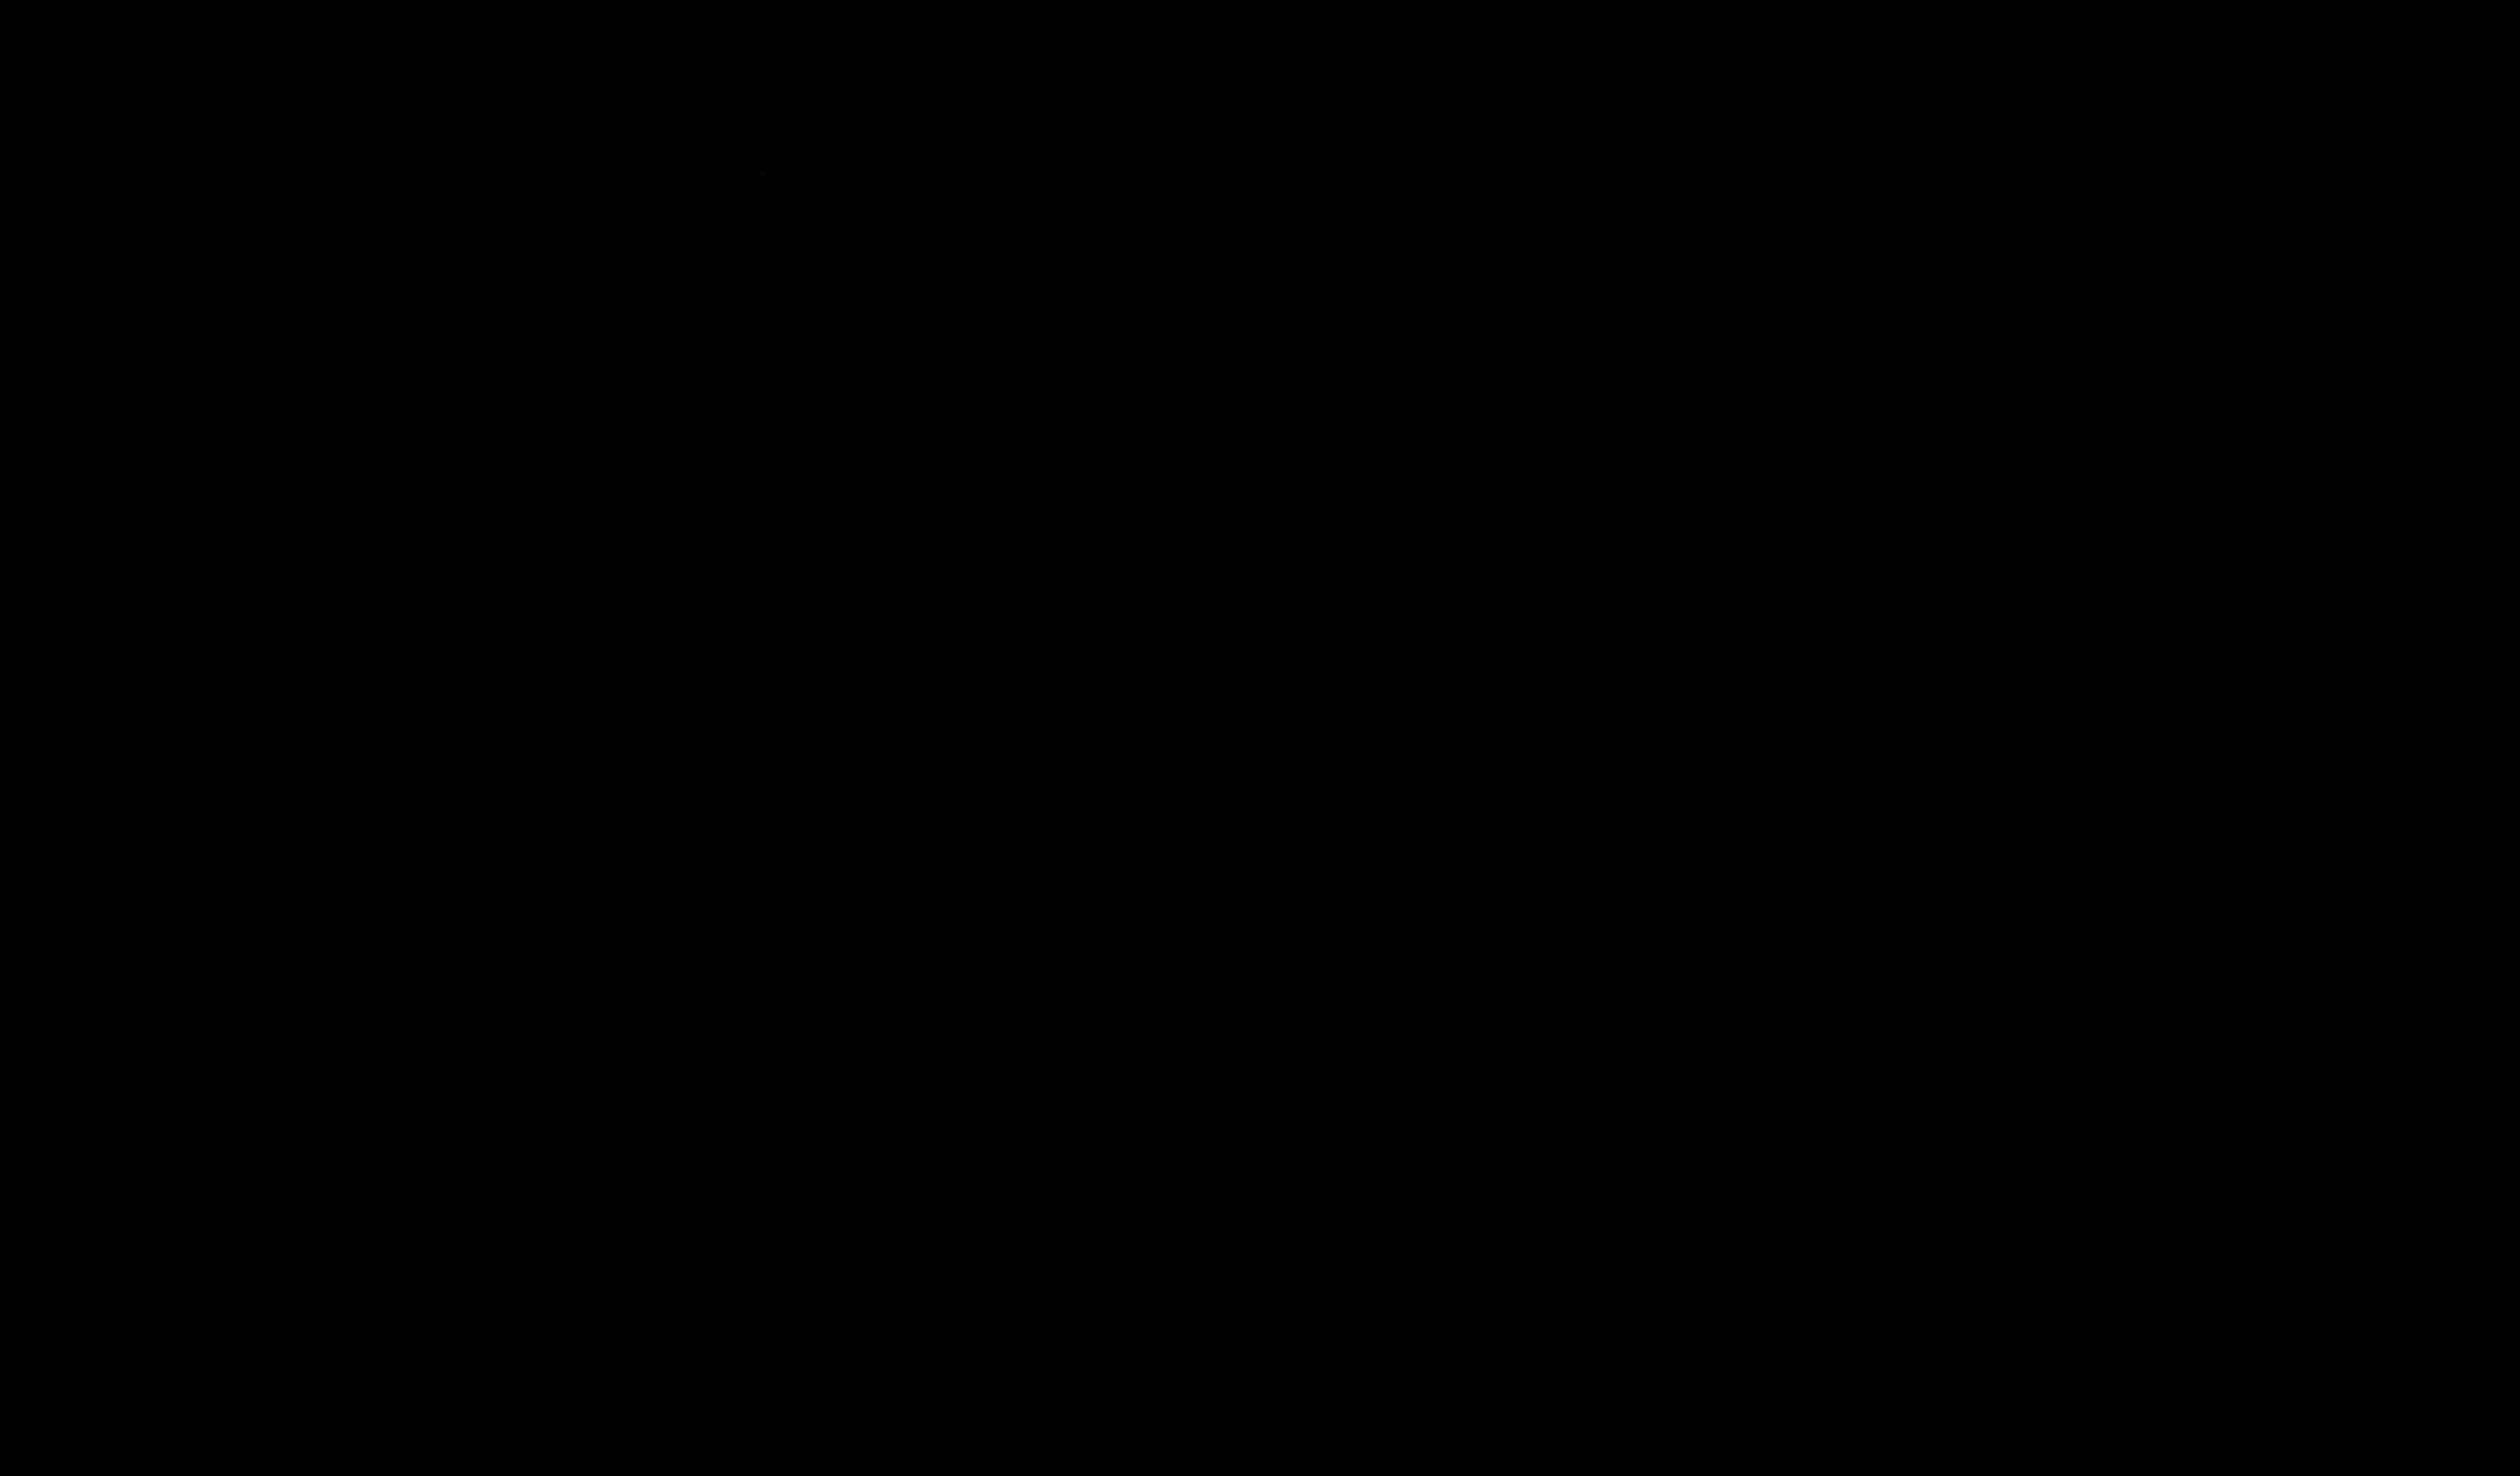
Open the issue you want to base your simulation on.
Use the keyboard shortcut cmd+k to open the actions menu (or click all actions on the top right).
Click Create Simulation.
The simulation form preloads with a copy of the issue you selected. From here, make any changes to the email body, send dates, recipients, etc.
The simulation automatically starts on your chosen date once you add at least one recipient.
To check the simulation status and results, from the left navigation click Simulations then open your simulation.

Email Threat Issues Analysis Updates
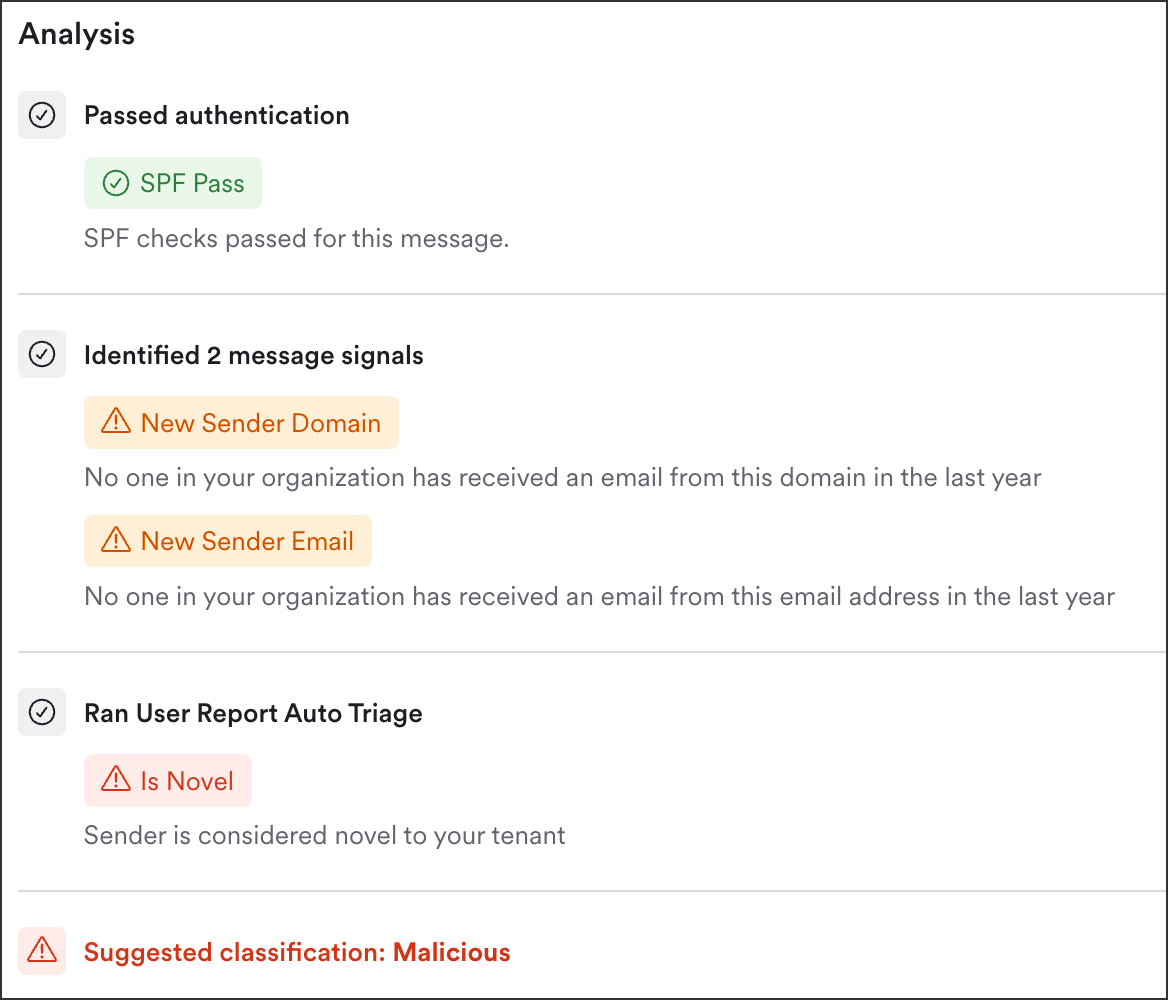
From an Email Threat issue detail view, phishing analysis is now divided into three, distinct sections:
Authentication Results
Message Signal Analysis
User Report Auto Triage (also known as Classification), if applicable
Smarter Defaults
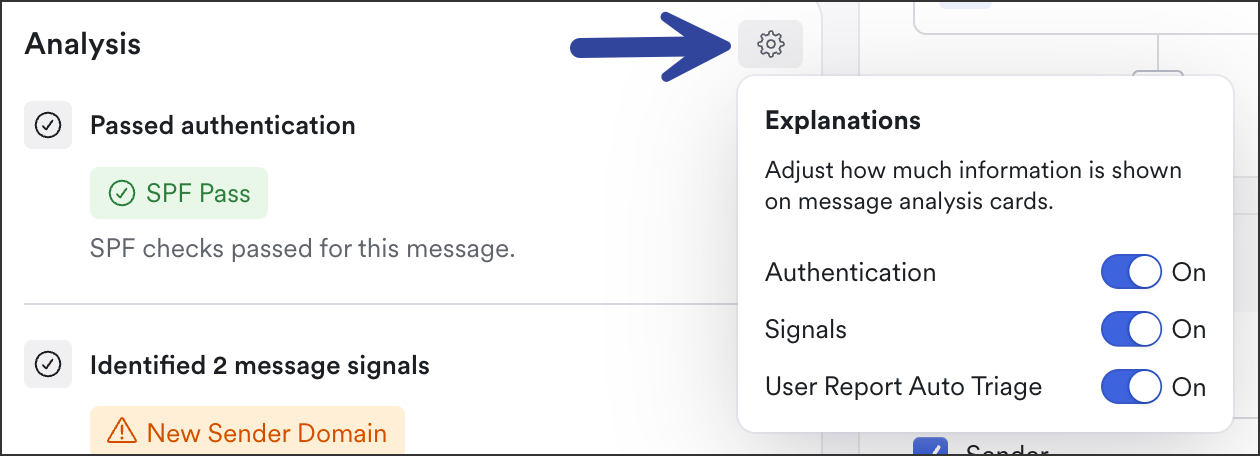
Choose whether you want more verbose explanations up front on the phishing analysis card.
From the analysis card in an Email Threat issue, click the settings cog icon then toggle explanation options on or off.
Initial Classification Location
The initial classification is now included in the timeline, at the bottom of the analysis card.
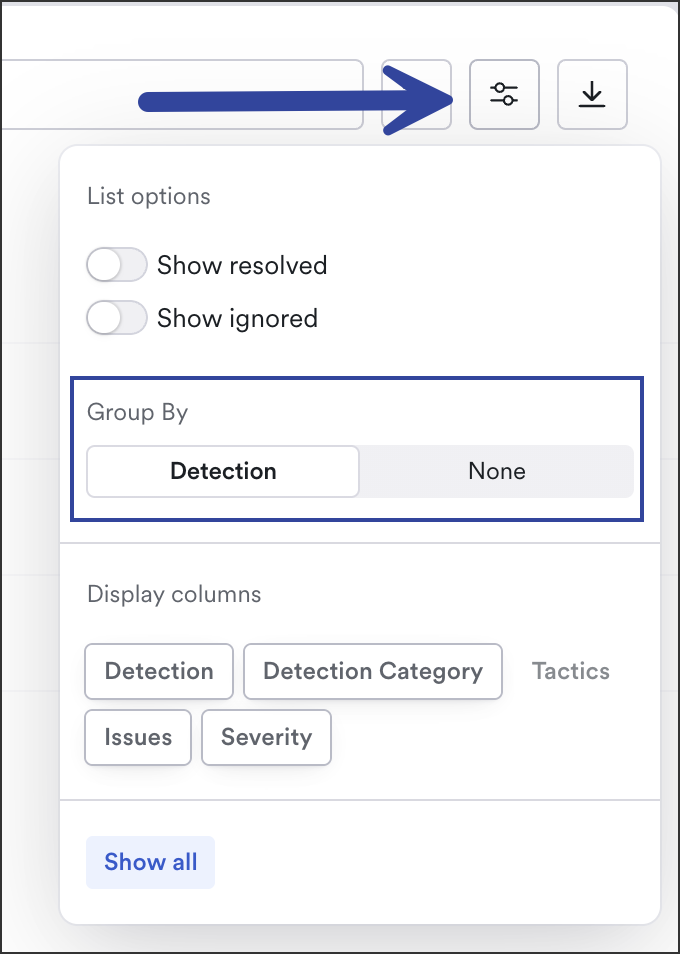
Group By Detection
Group {Issues} By Detection has moved on the issue view.
To the right of search, click Display Options:
Detection Improvements
Multi-Factor Authentication
Weak factor detection is now split by factor type—more granularity, better response.
Inbound Email Threats
New Detections:
XSS (cross-site scripting) attempts in subject lines
Procedurally generated subject gibberish
Crypto invoice callback phishing
TikTok impersonation
Updated Detections:
Overdue invoice scam logic got smarter
Display name spoofing now better distinguishes legit ticket systems
Docusign and encrypted PDF performance tuned up
Microsoft Teams impersonation logic improved
Overlapping “To” and “CC” recipient trickery now flagged faster
Excluded Linear’s legit links from document review URL warnings
Various scam link and attachment rules optimized for speed and accuracy
Last updated
Was this helpful?