

Unified Phishing Issue Experience
Email Threat Improvements
Cases are now Issues, located in the Issue view
Collections of similar emails based on their detection method, content, etc. (formerly known as cases) are now all unified in the global issue list. From the left navigation, select either Email Threats to view all or focus in on User Reports specifically:
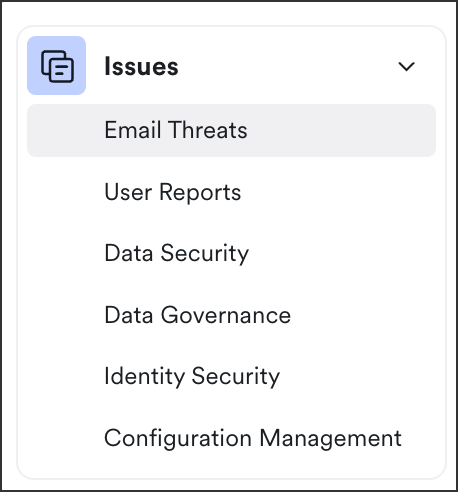
Phishing Detections new location
Phishing issues are triggered by one of three detection methods:
User reported messages
Admin created rules (custom detections)
To view — from the Detections list, filter by Detection Category to the Email Security type:
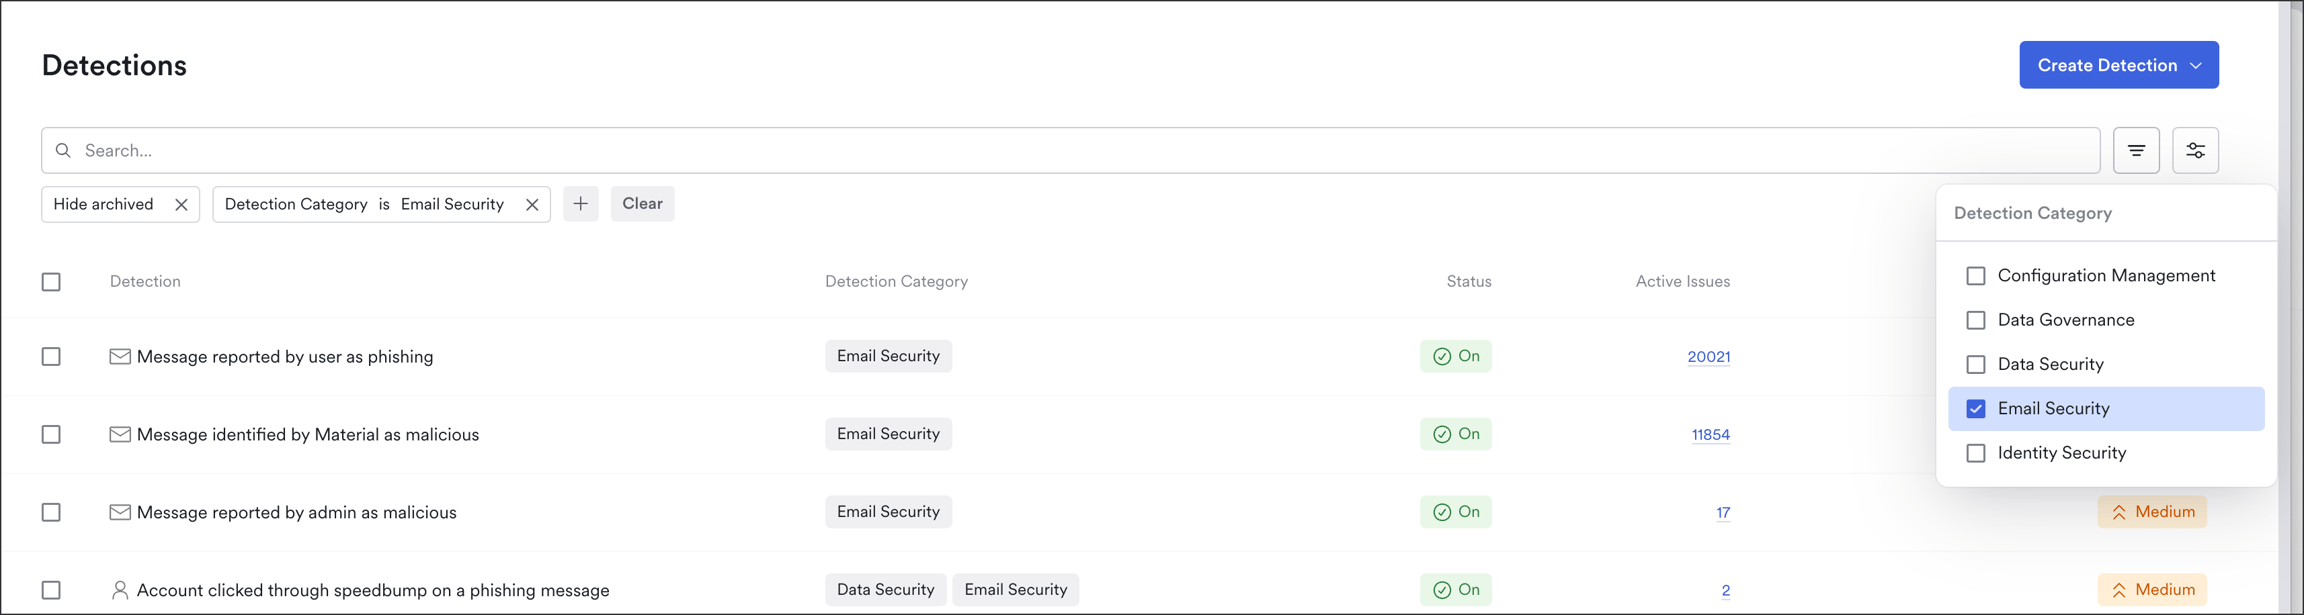
Default responses when there are multiple detection types
Material automatically assigns the lead detection based on which method flagged the threat first. For example, if Material detects the issue then a user also reports it after Material detected it — the issue's initial detection is "Material detected".
This is important because remediation actions follow the response configured for the message source. If you've configured a different response for user reports than for Material detected messages, the default response for the issue will be for the lead detection type (in our example above, the Material detected default).
Auto Threat Hunt runs for 30 days post-Issue creation, whether or not the issue's been resolved.
Entity and Sender columns
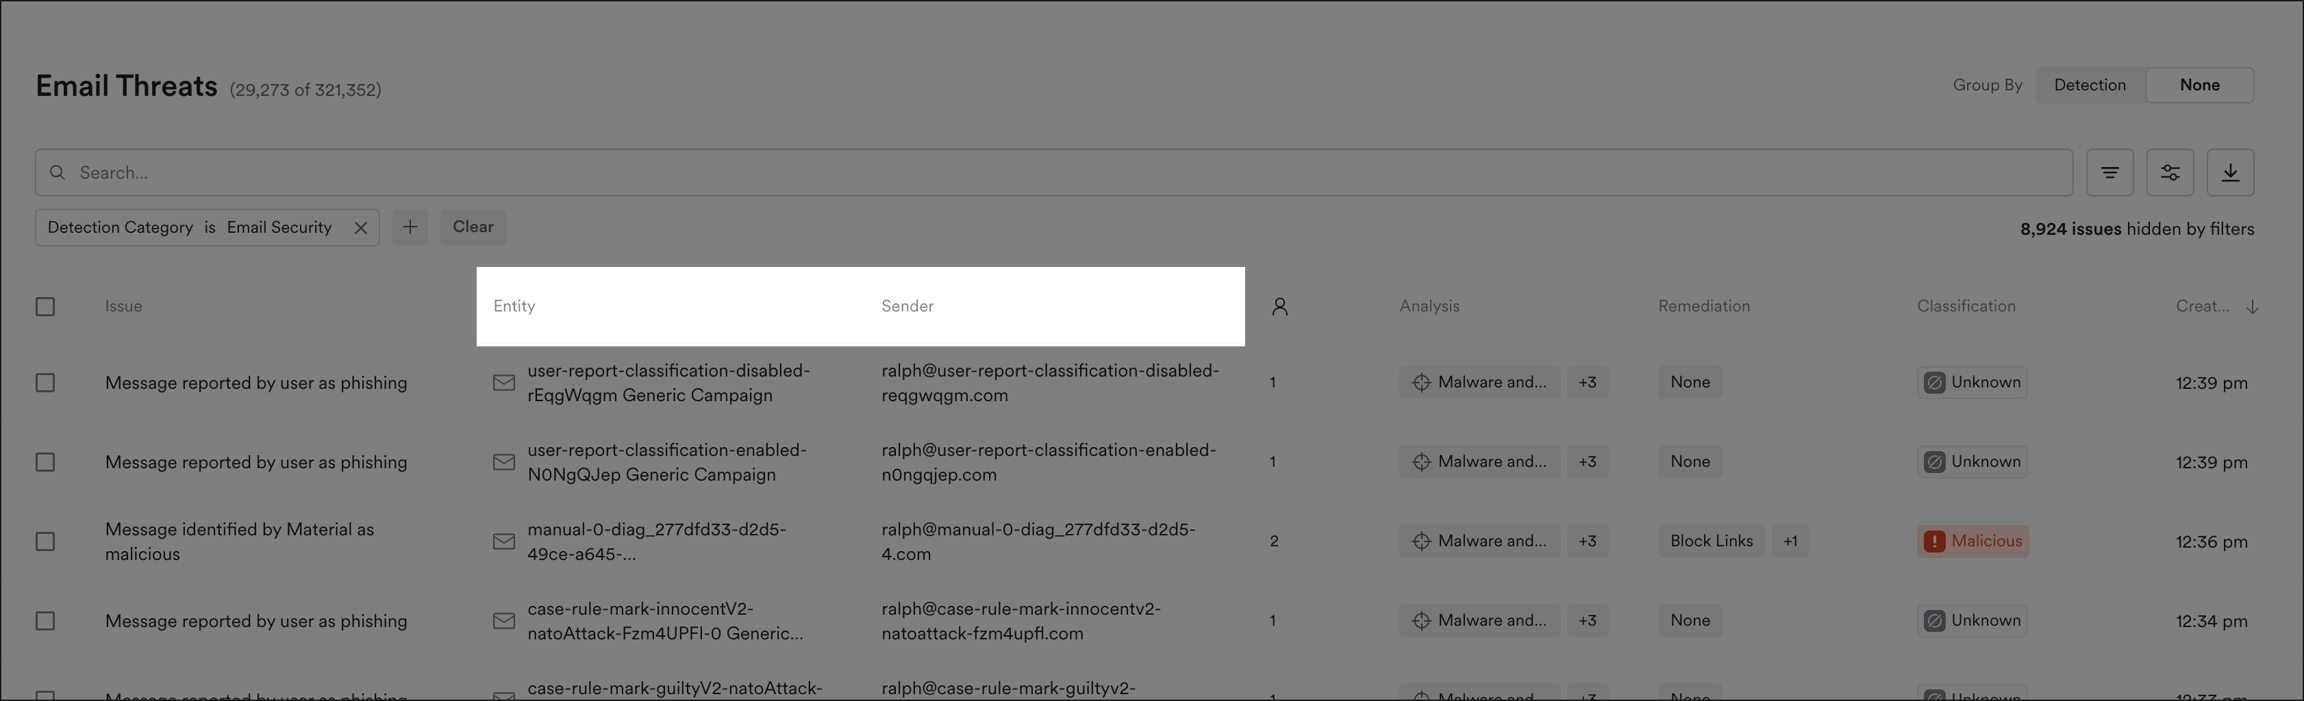
View by issue detection source
We're replacing the Detected By with a new Detected By filter — very soon. We'll update you in release notes when that change is officially made.
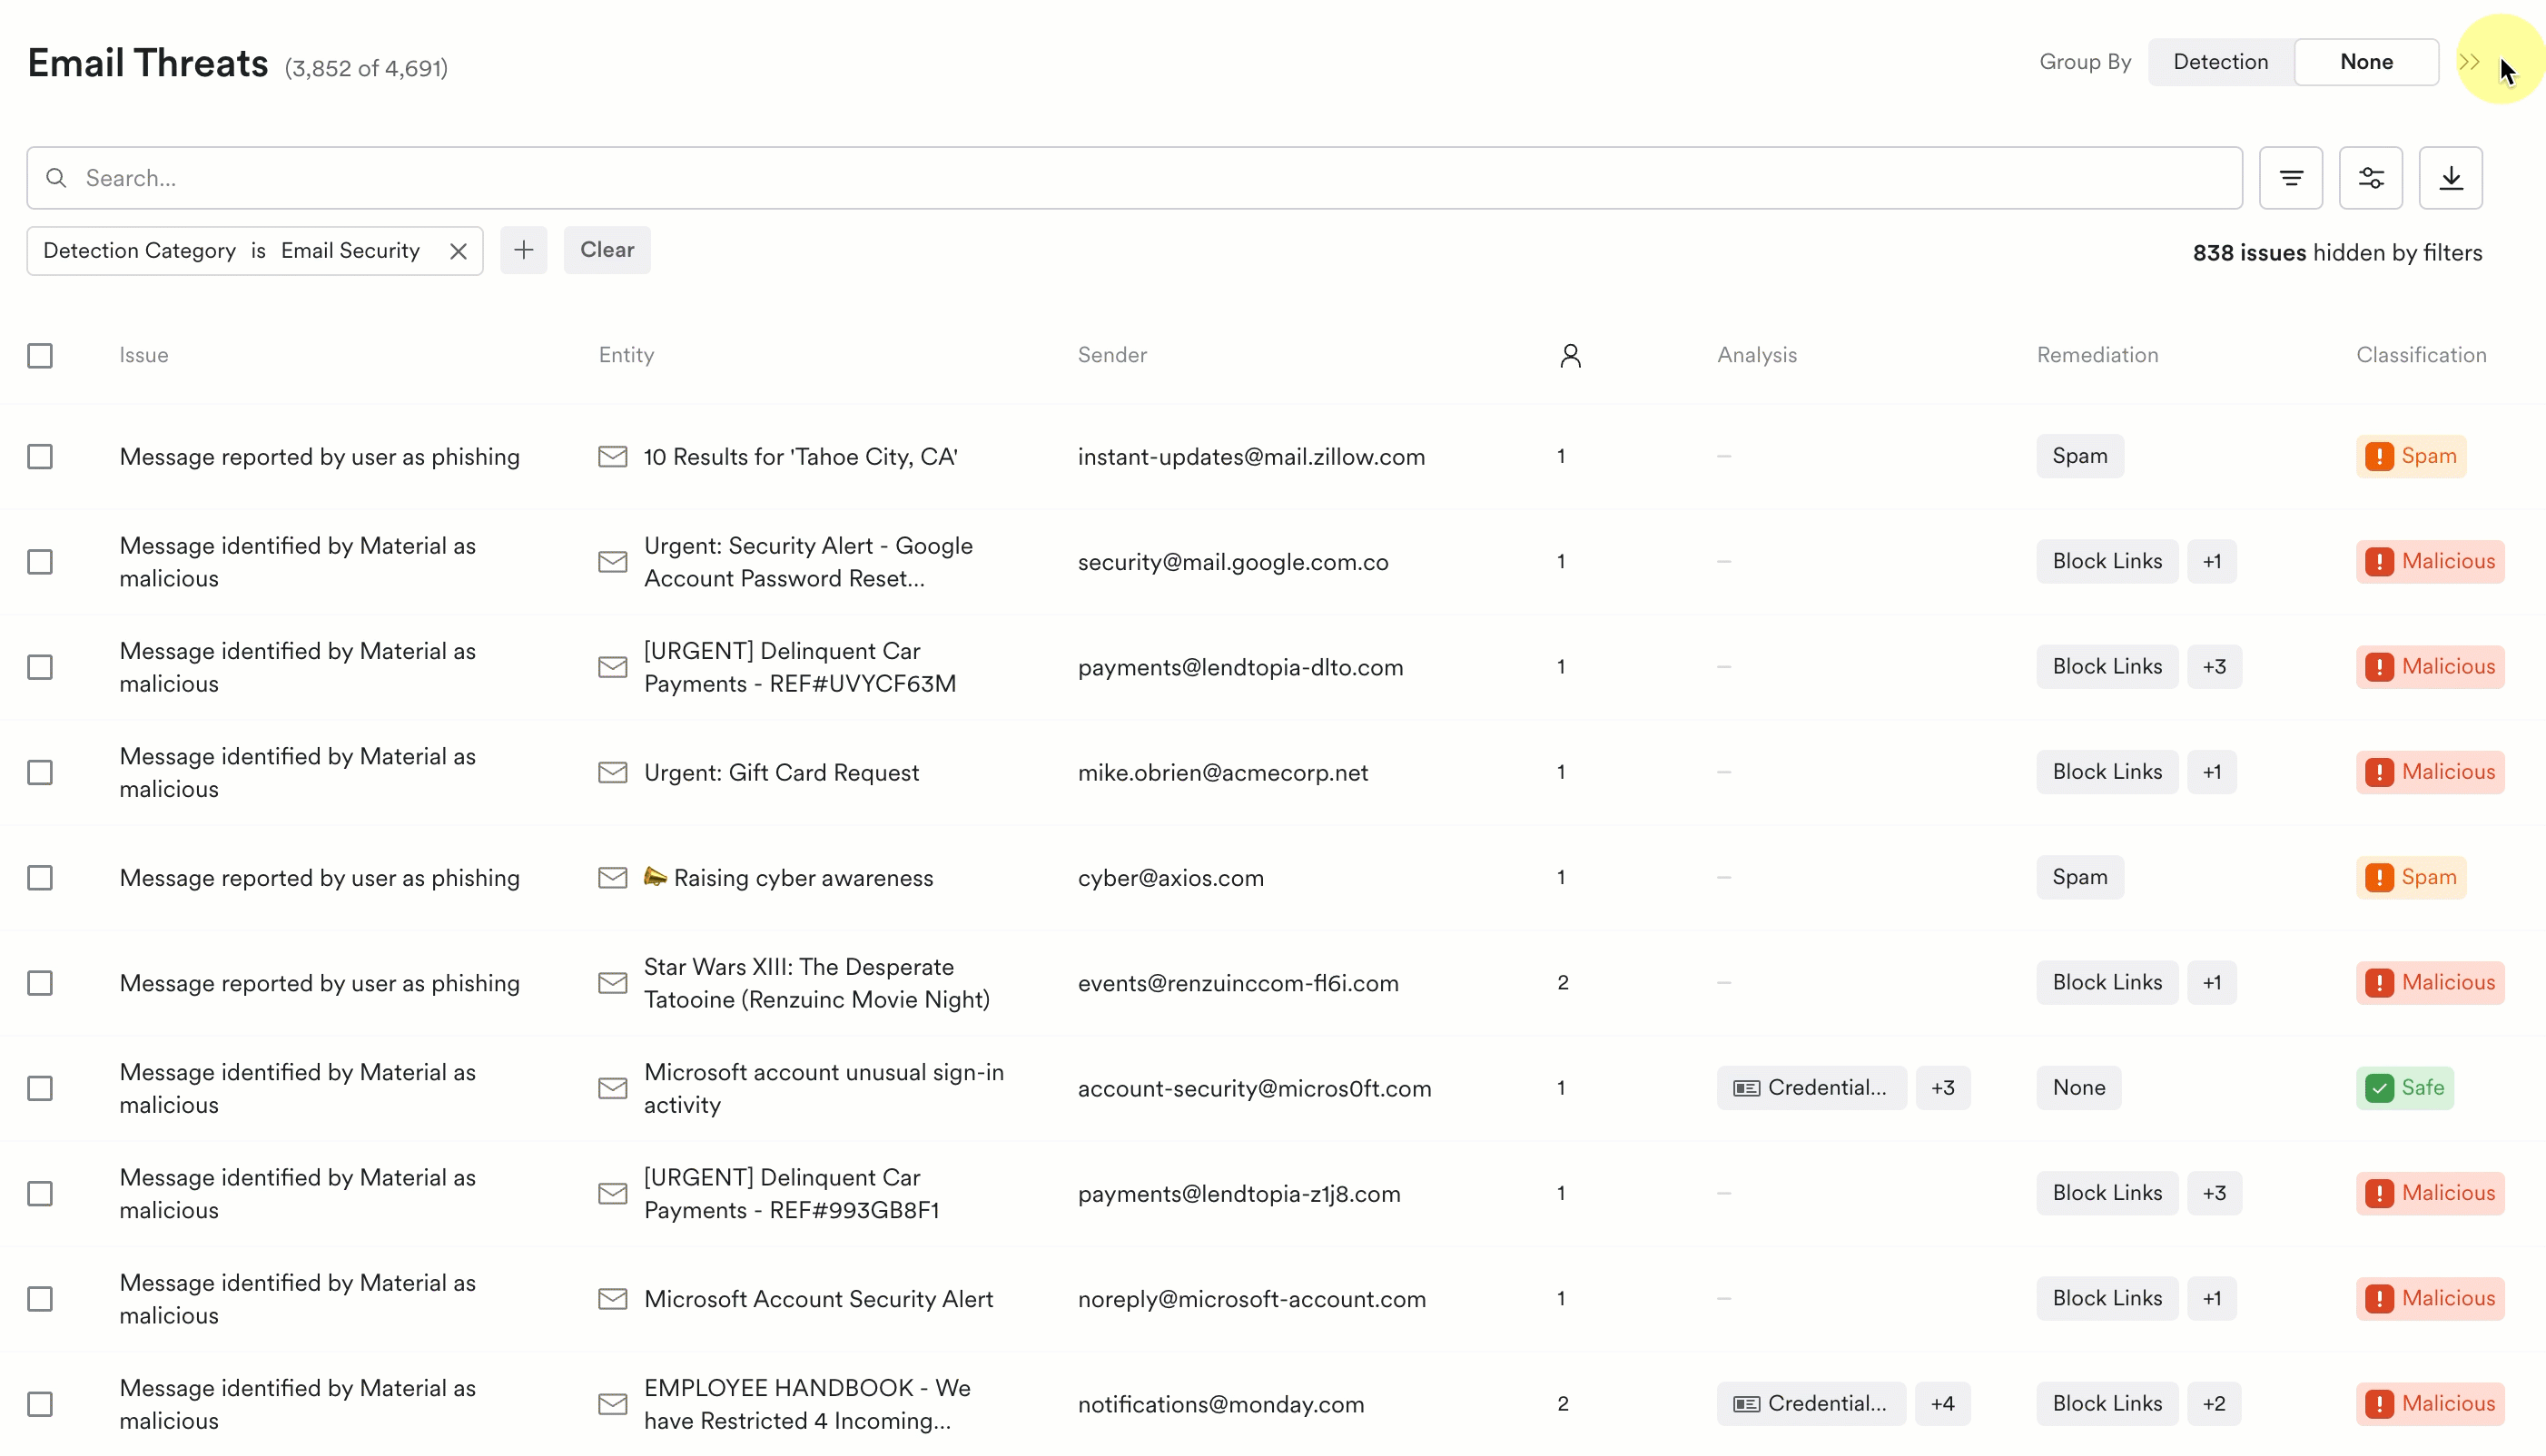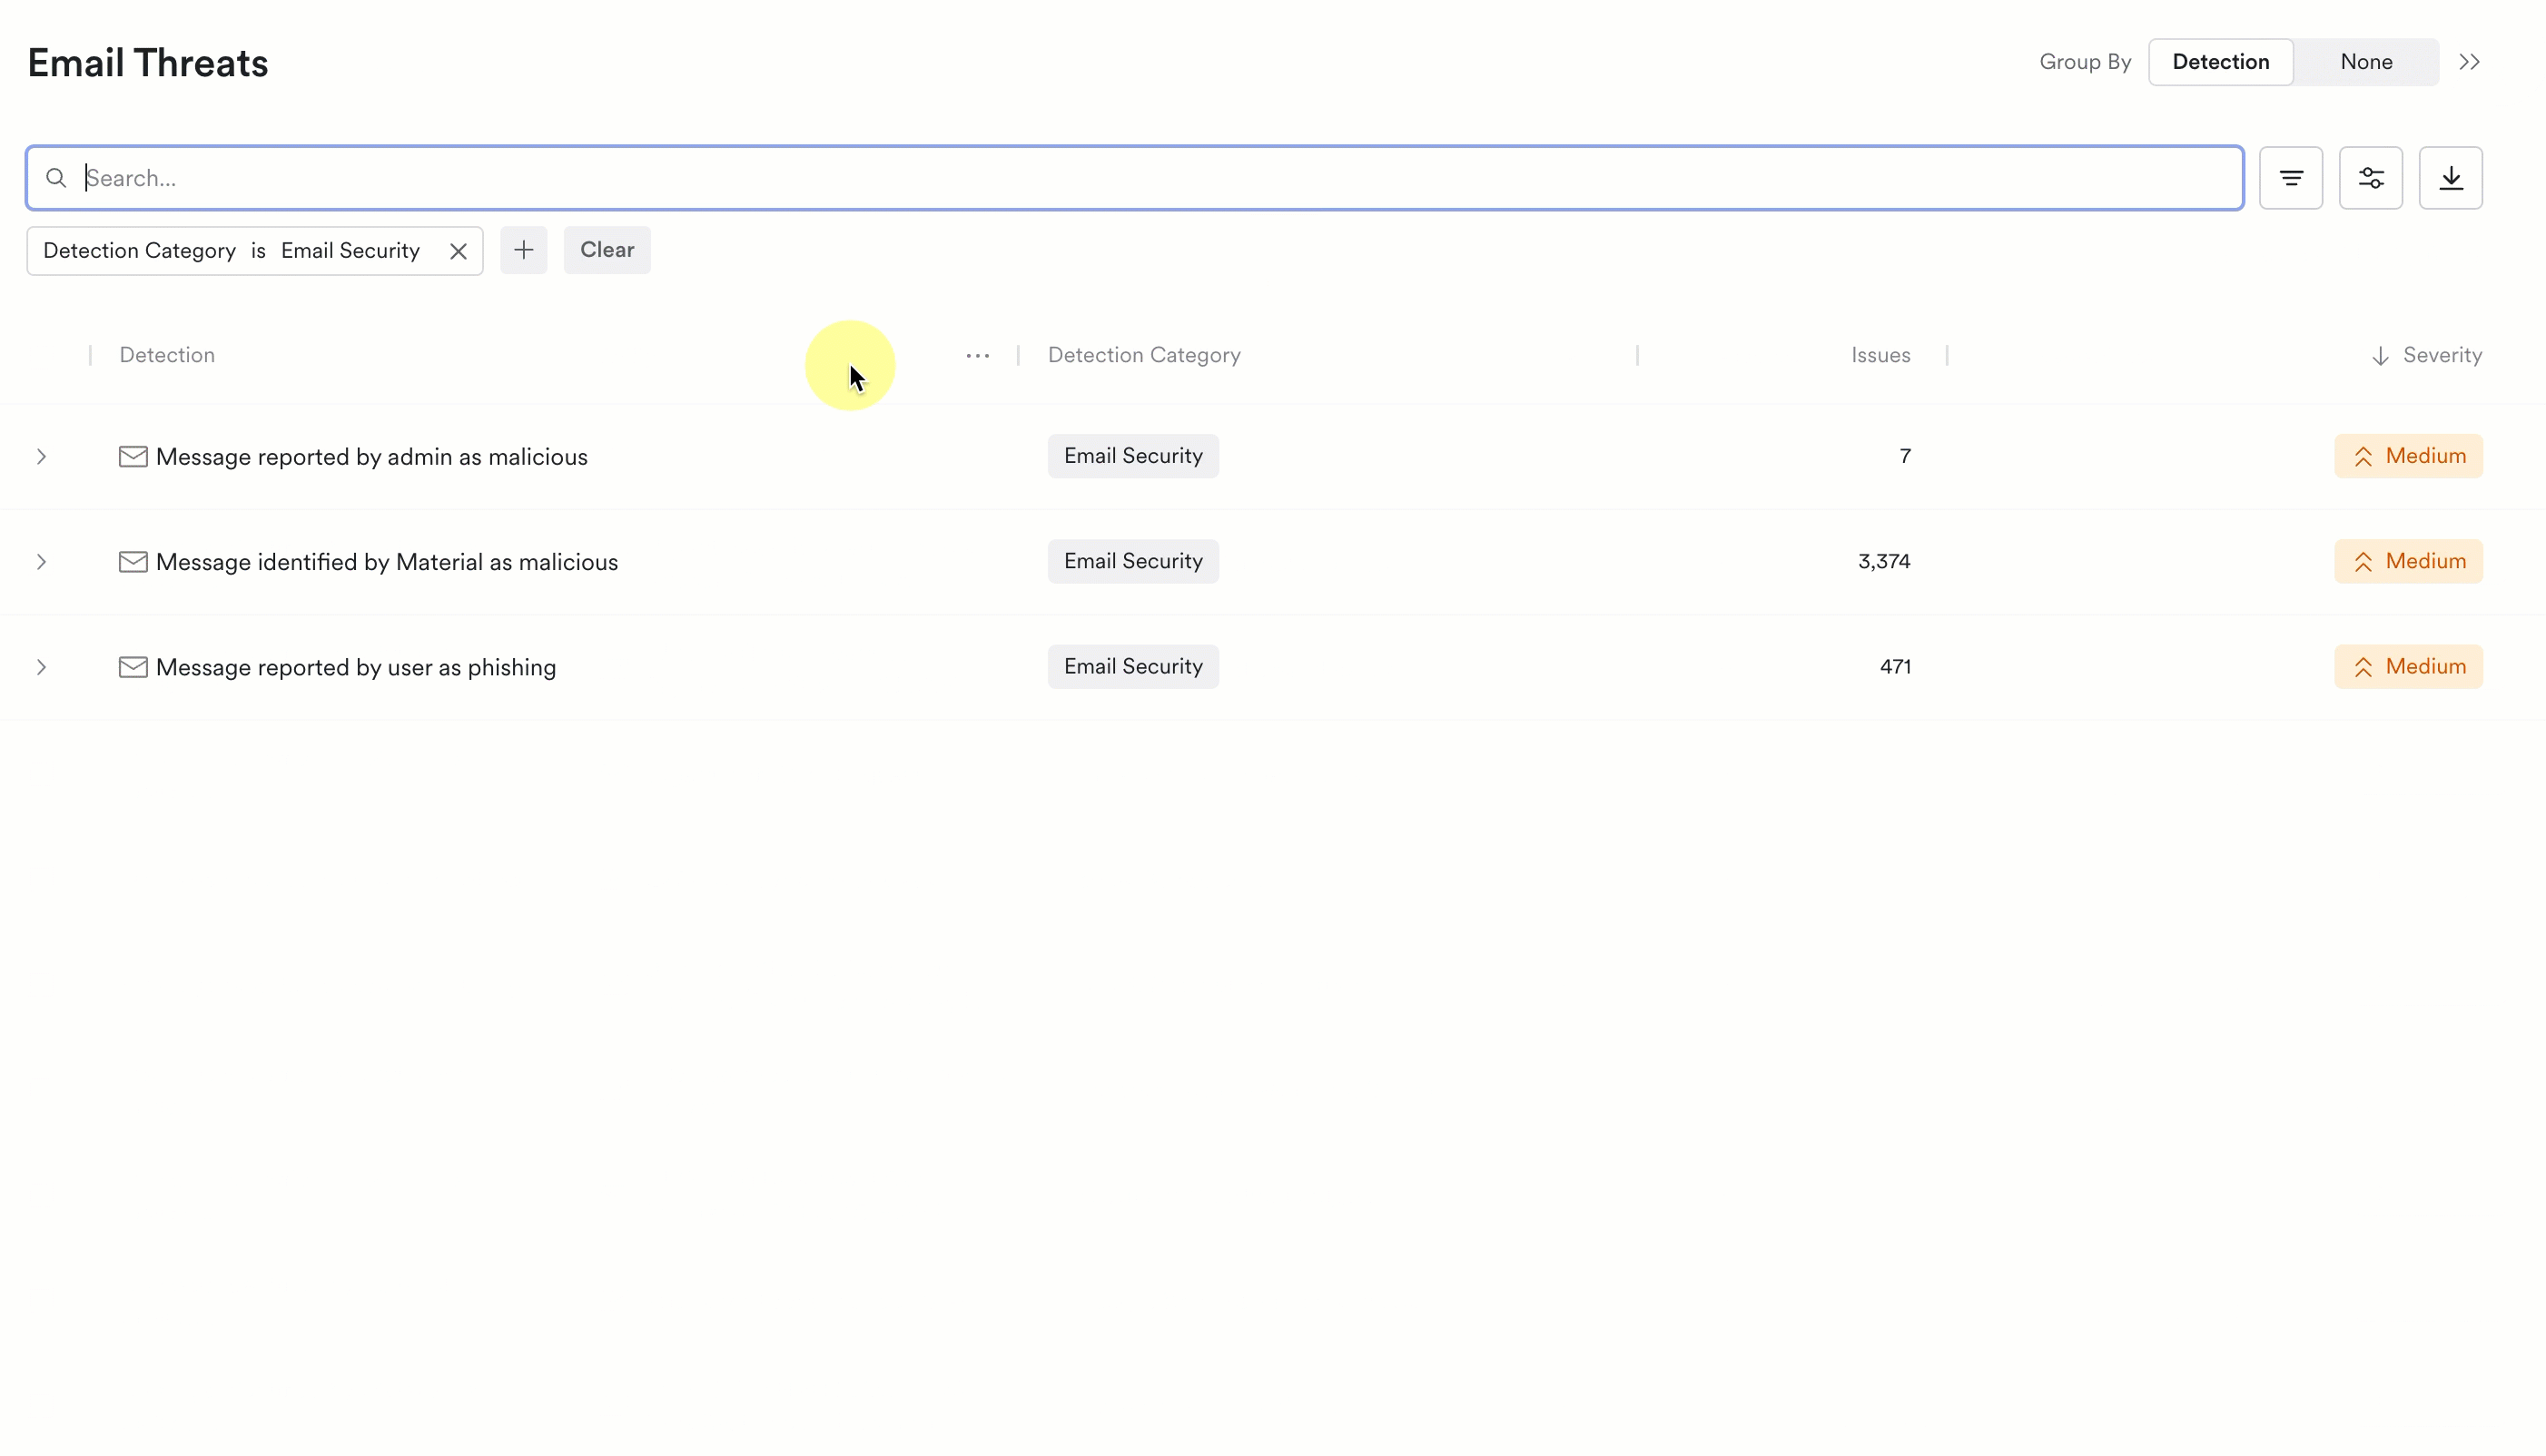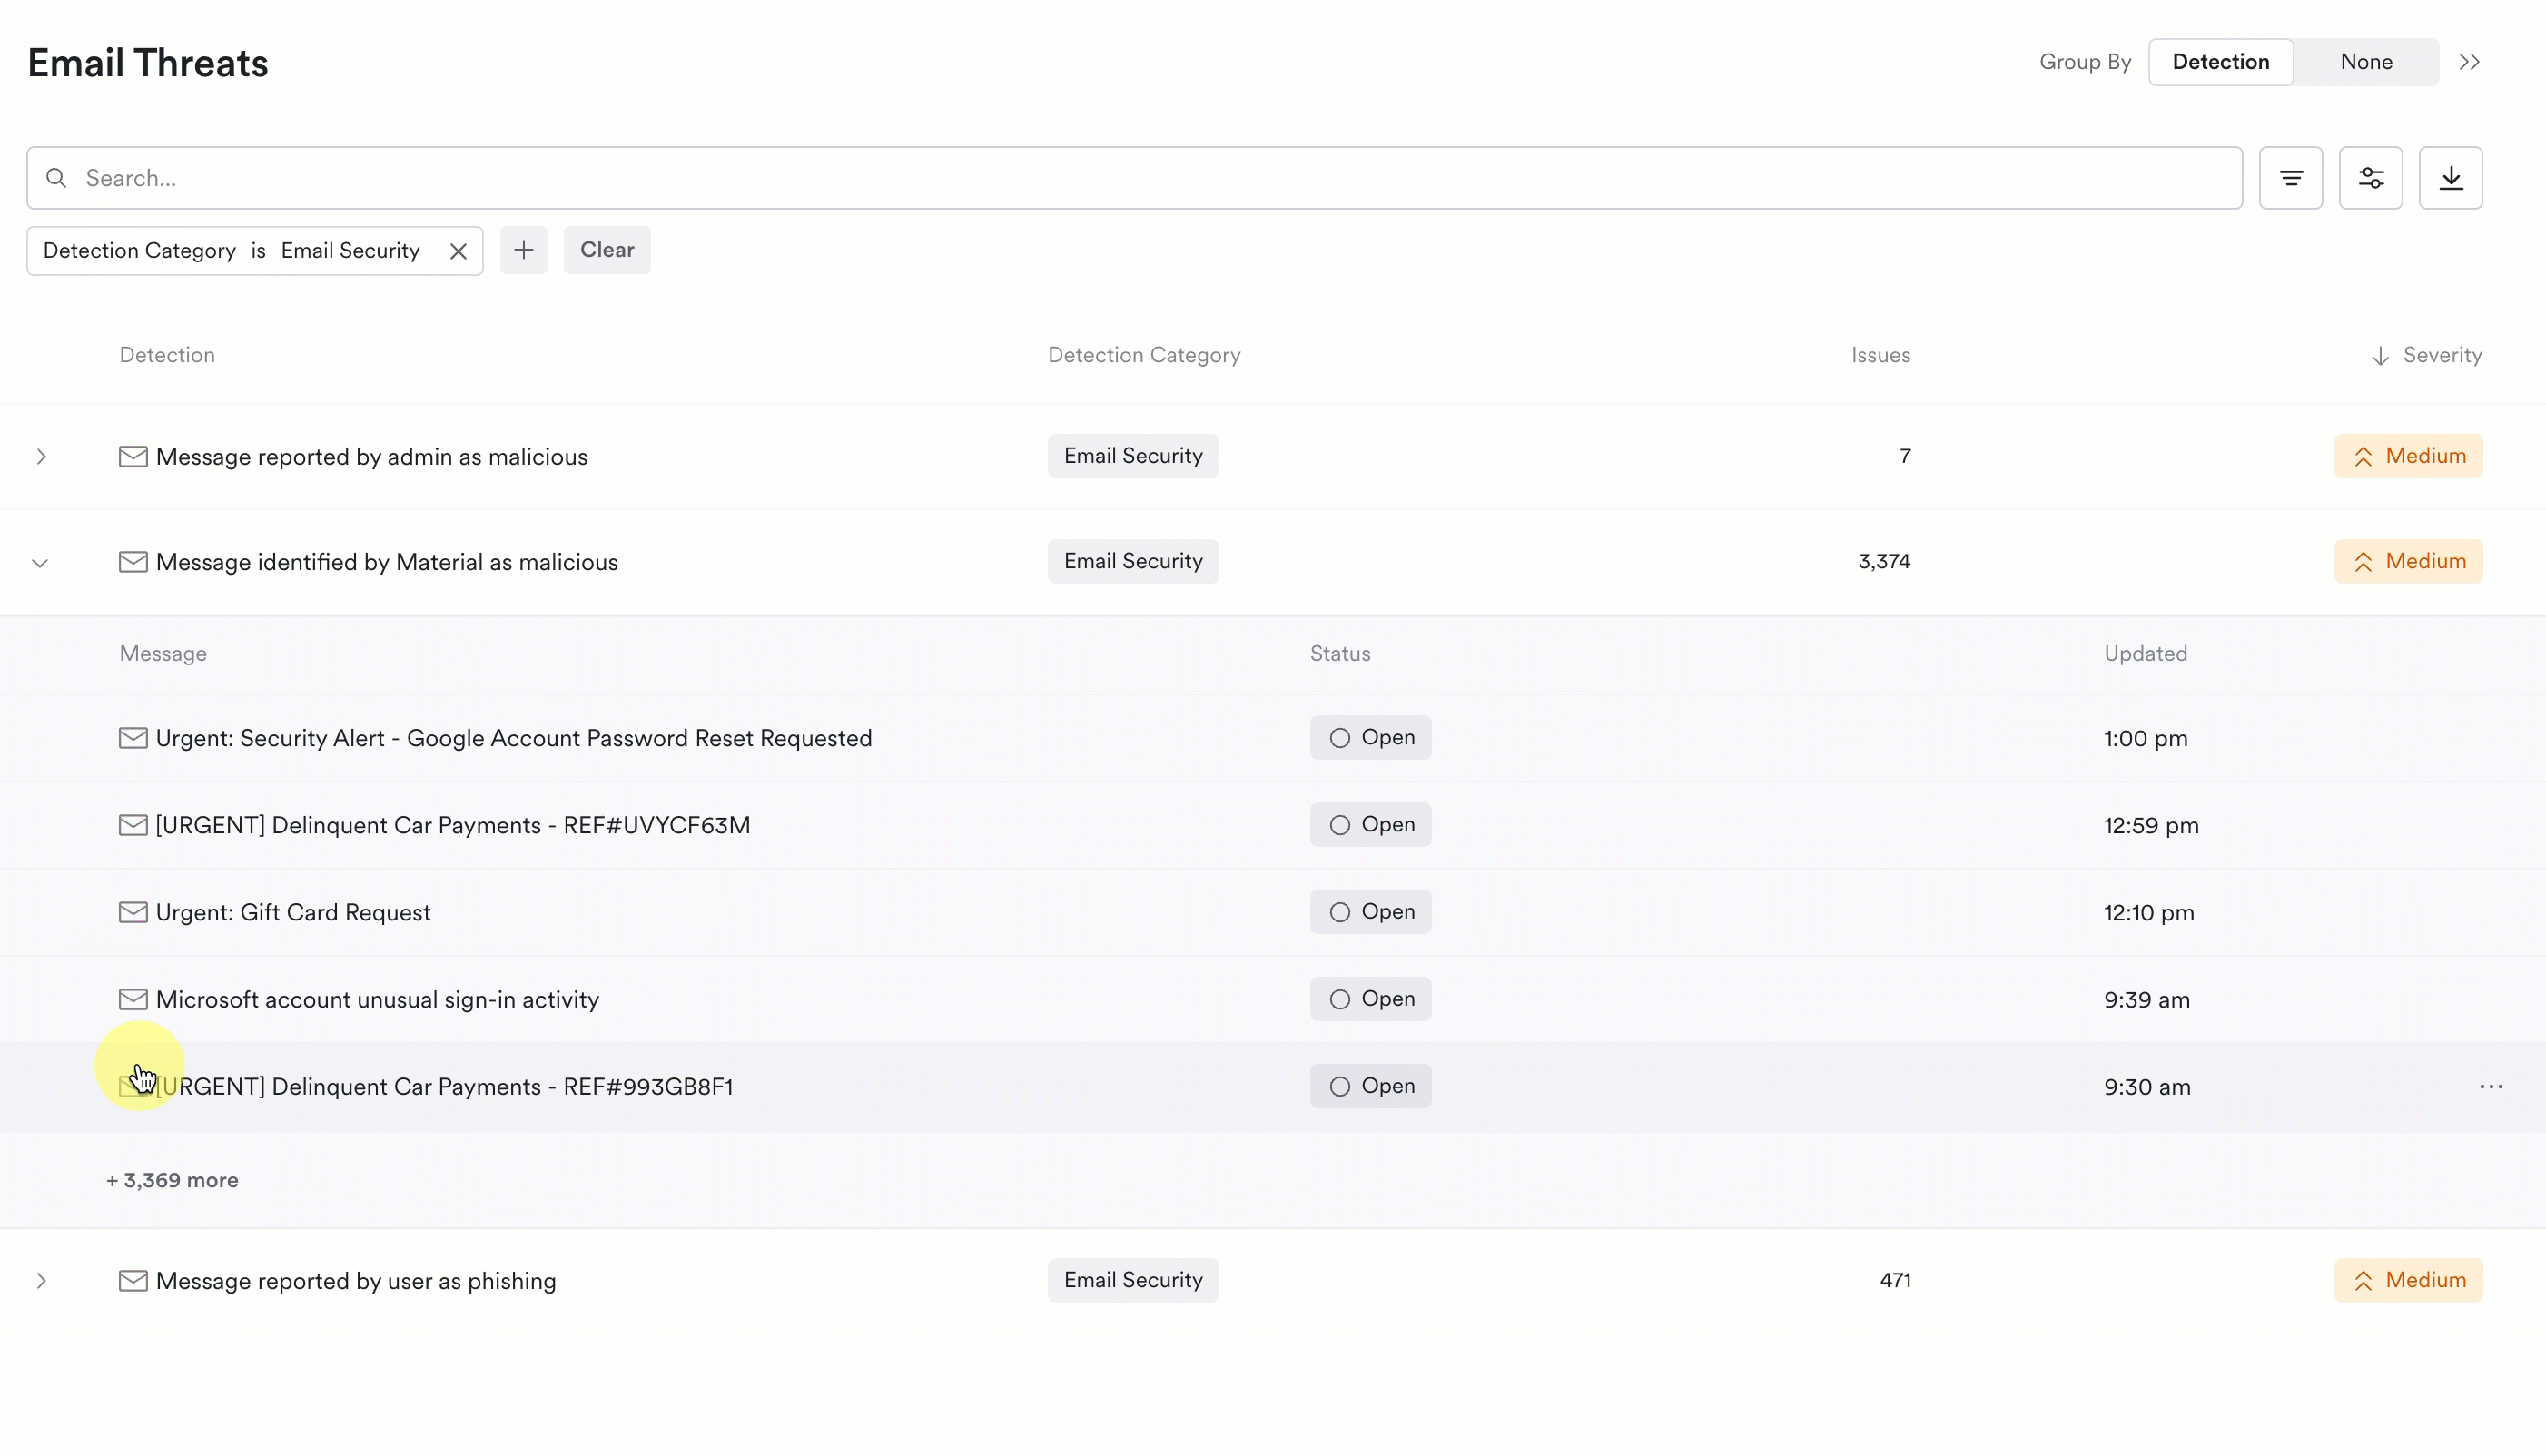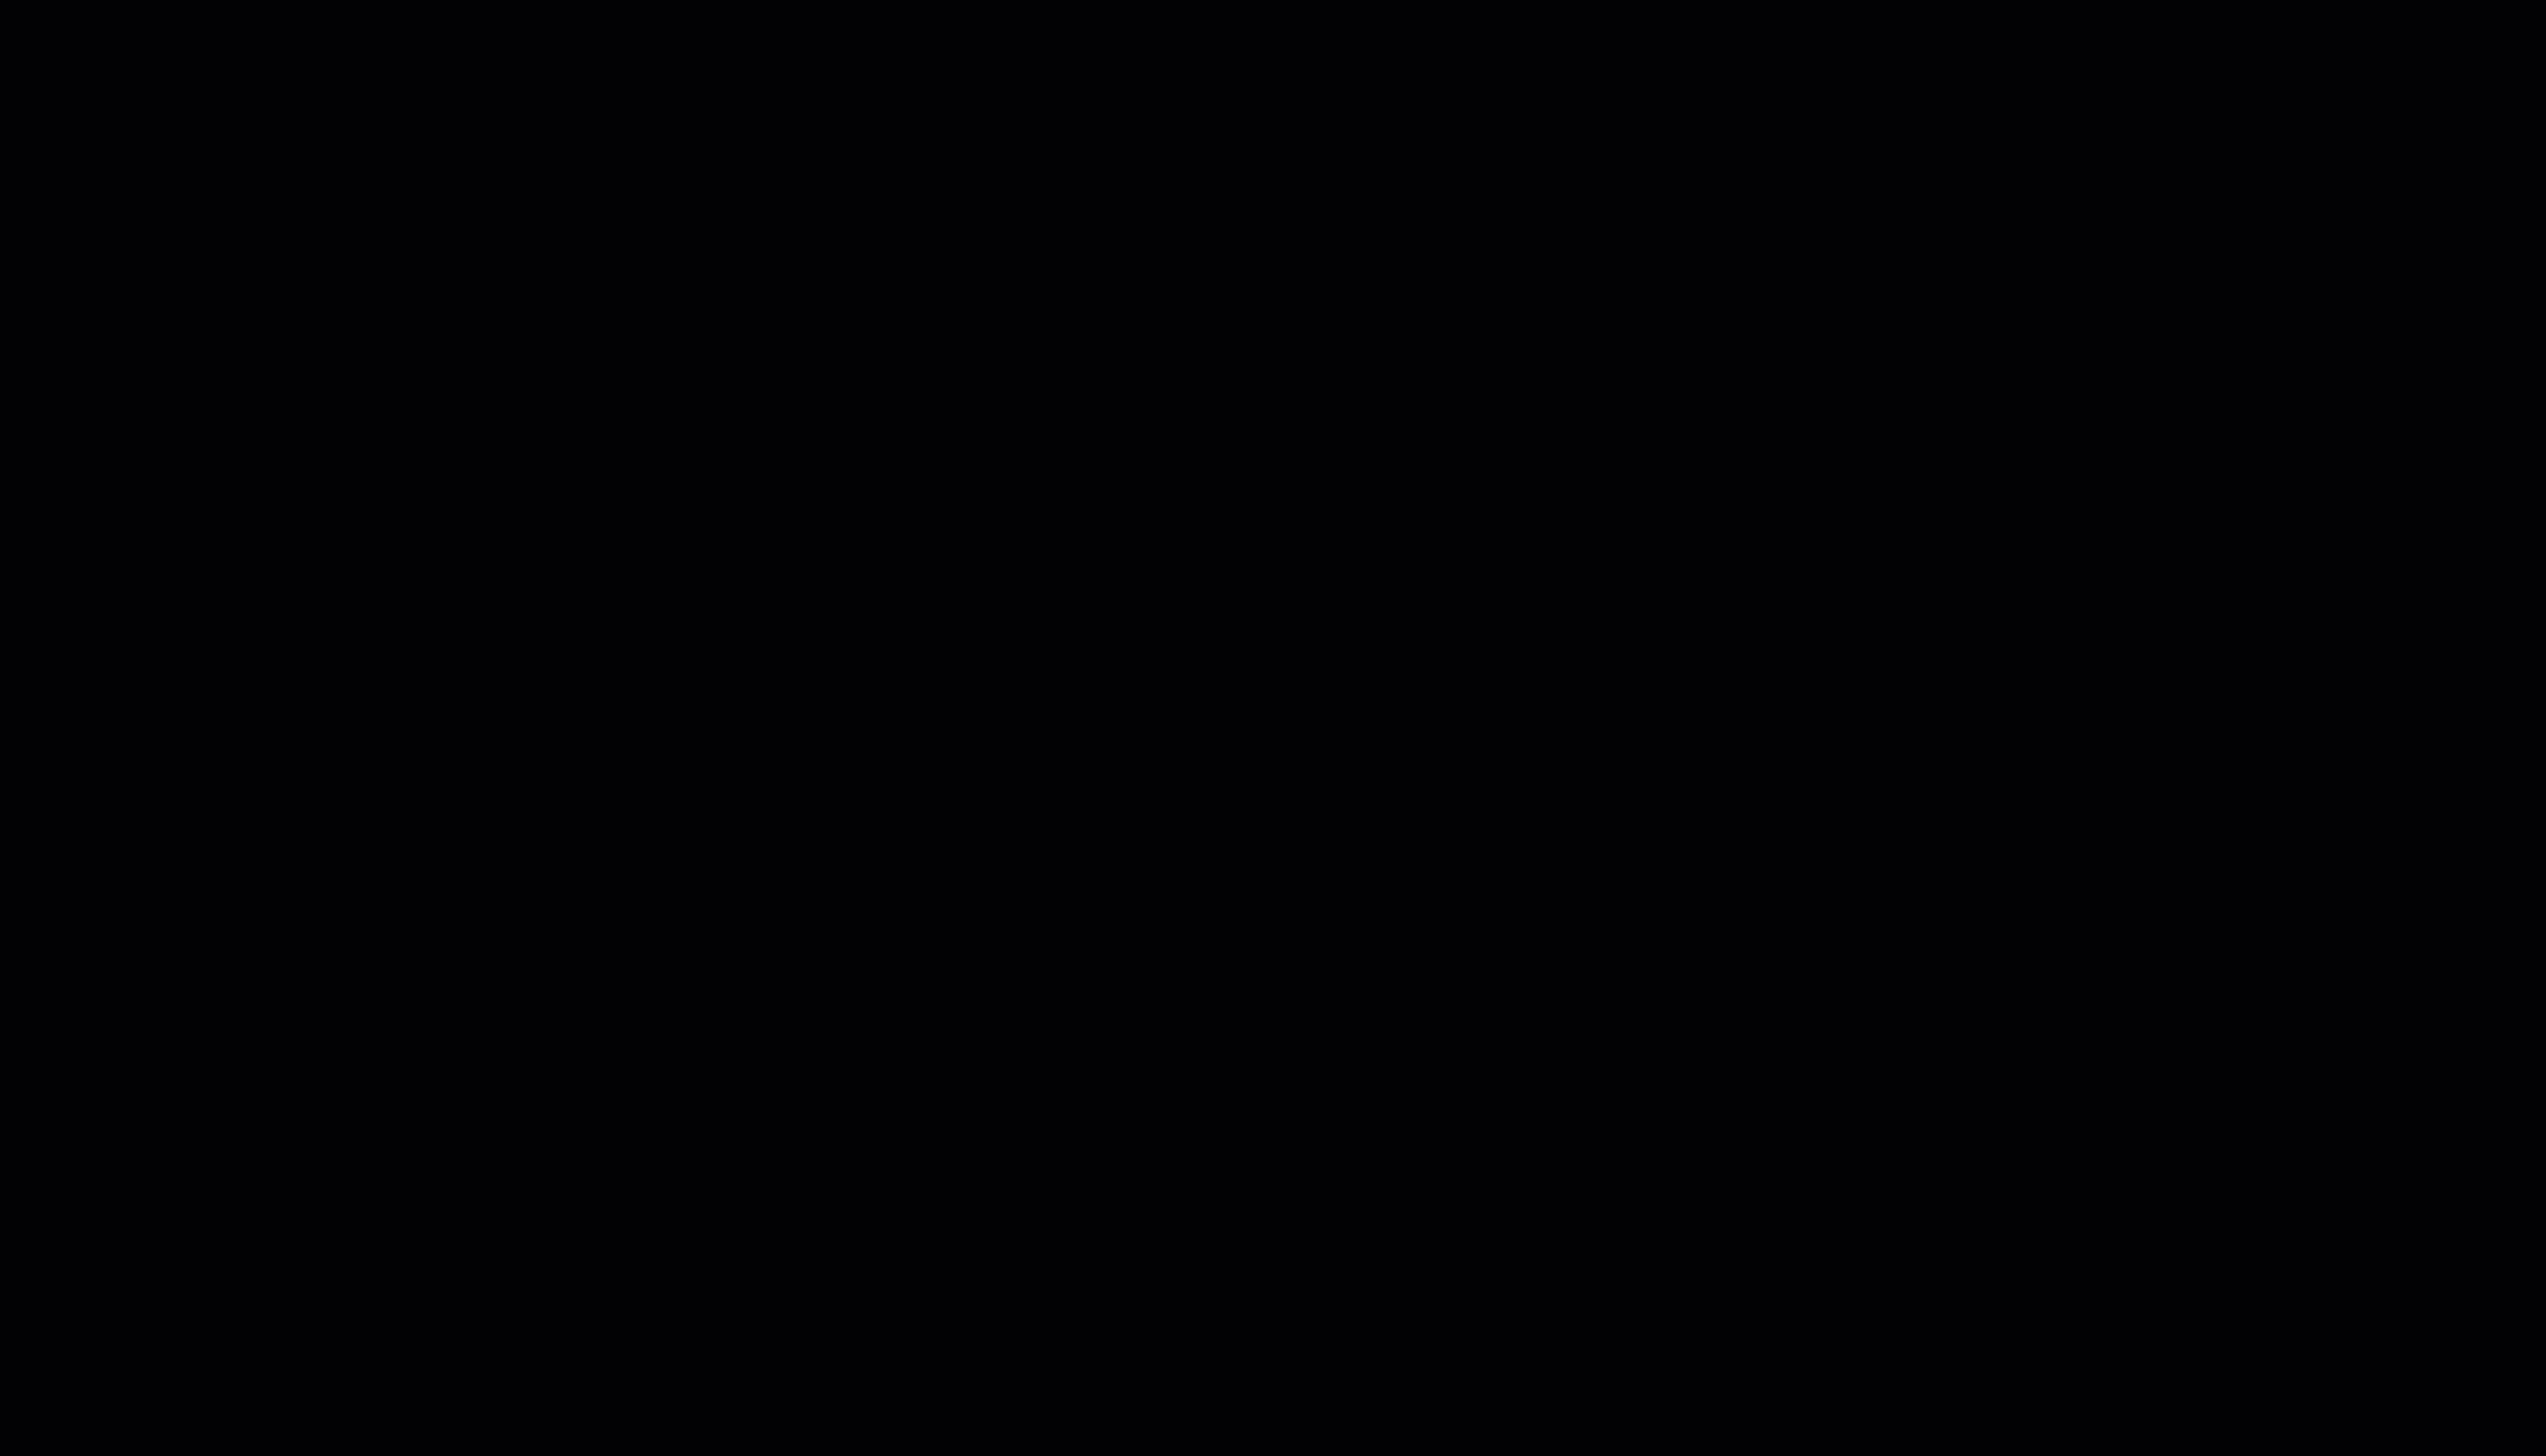
Until then, to view issues by a specific detection source, from the Email Threats issue page, group by Detection then click into the detection type to view issues detected by a specific source:
Customize Auto Threat Hunt Attributes
From the issue detail view, you can manually select (or de-select) attributes to match similar messages with. Matching messages are then added to the issue. One example for this is to stop adding messages to an issue that are matching only on a generic subject line.
Last updated
Was this helpful?