

Version 1.27
Settings Improvements and View License Details (Coming Soon)
Admins can now view and assign license details in Default Account Settings at the Global, Tenant, and Account levels:
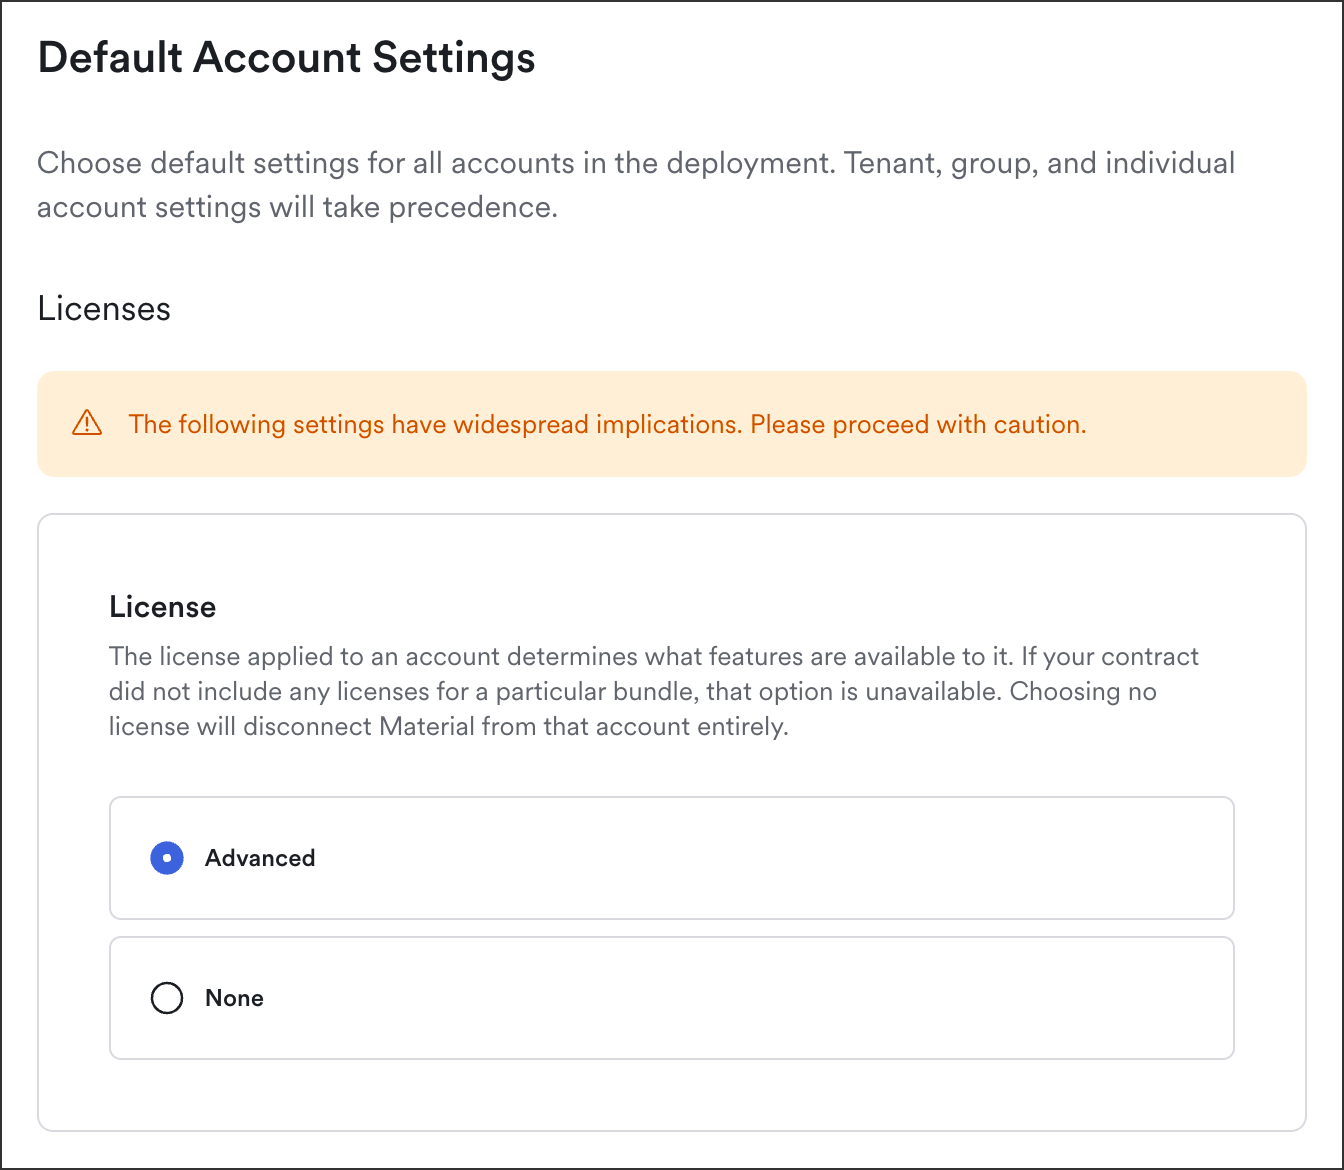
We restructured settings for ease of use including:
Syncing (located in Default Account Settings)
Remediation (located in Default Account Settings)
Google Drive Syncing (restructured)
ATO Resilience (restructured)
VIP Designation (now located in Organization Profile)
Learn more about default settings and applying settings at the Global, Tenant, or Account levels in the Deployment Guides.
Email Threat Detection Improvements
We updated Email Threat Detections to continue staying ahead of evolving email threats. To view any issues created from these detections:
From the workspace expand Issues then click Email Threats.
Open an issue to view analysis details.
Banking Detail Change Requests
Detects attempts to request changes to payment or banking information from newly registered domains
EICAR Test String Detection
Flags emails containing the standard EICAR test string used for testing antivirus software
Employee Policy Update Lures
Detects malicious emails using fake employee policy updates as a lure
Expanded Impersonation Coverage
New detection patterns now cover impersonation of services like HubSpot, WeTransfer, Norton, and Adobe & related brands
Fake Gmail Attachments
Identifies messages that attempt to spoof Gmail elements.cover impersonation of services like HubSpot, WeTransfer, Norton, and Adobe & related brands
Requests for Phone Numbers or PII
Flags messages attempting to solicit a recipient’s phone number or other personal identifiable information
Slack Connect Abuse
Detects suspicious messages using Slack Connect with mismatched reply-to addresses and organization names
Suspicious Google Drive Notifications
Flags Drive notifications containing unusual language and unfamiliar reply-to addresses.
VIP Impersonation Using Free Email Providers
Detects when a subject line references a configured VIP, but the sender’s email address does not match expected domains and uses a free provider
Zelle Coercion via Phone Numbers
Identifies emails leveraging legitimate Zelle infrastructure that attempt to trick recipients into calling malicious phone numbers
Last updated
Was this helpful?