

Version 1.19
We've made some exciting changes in our new Unified Detections! All of your current default settings and configurations migrate; they may just be in a new location.
Posture Management Migration
We merged the Posture Management product with our new Detections to increase effectiveness. Now, you'll see the previous Posture Management reports broken into more precise detections that you can take action on and track over time.
For example, the previous "Which Google Workspace accounts don't have MFA enabled" report now displays in two detections:
Account does not have a registered MFA factor in Google Workspace
Account is an admin and does not have a registered MFA factor in Google Workspace
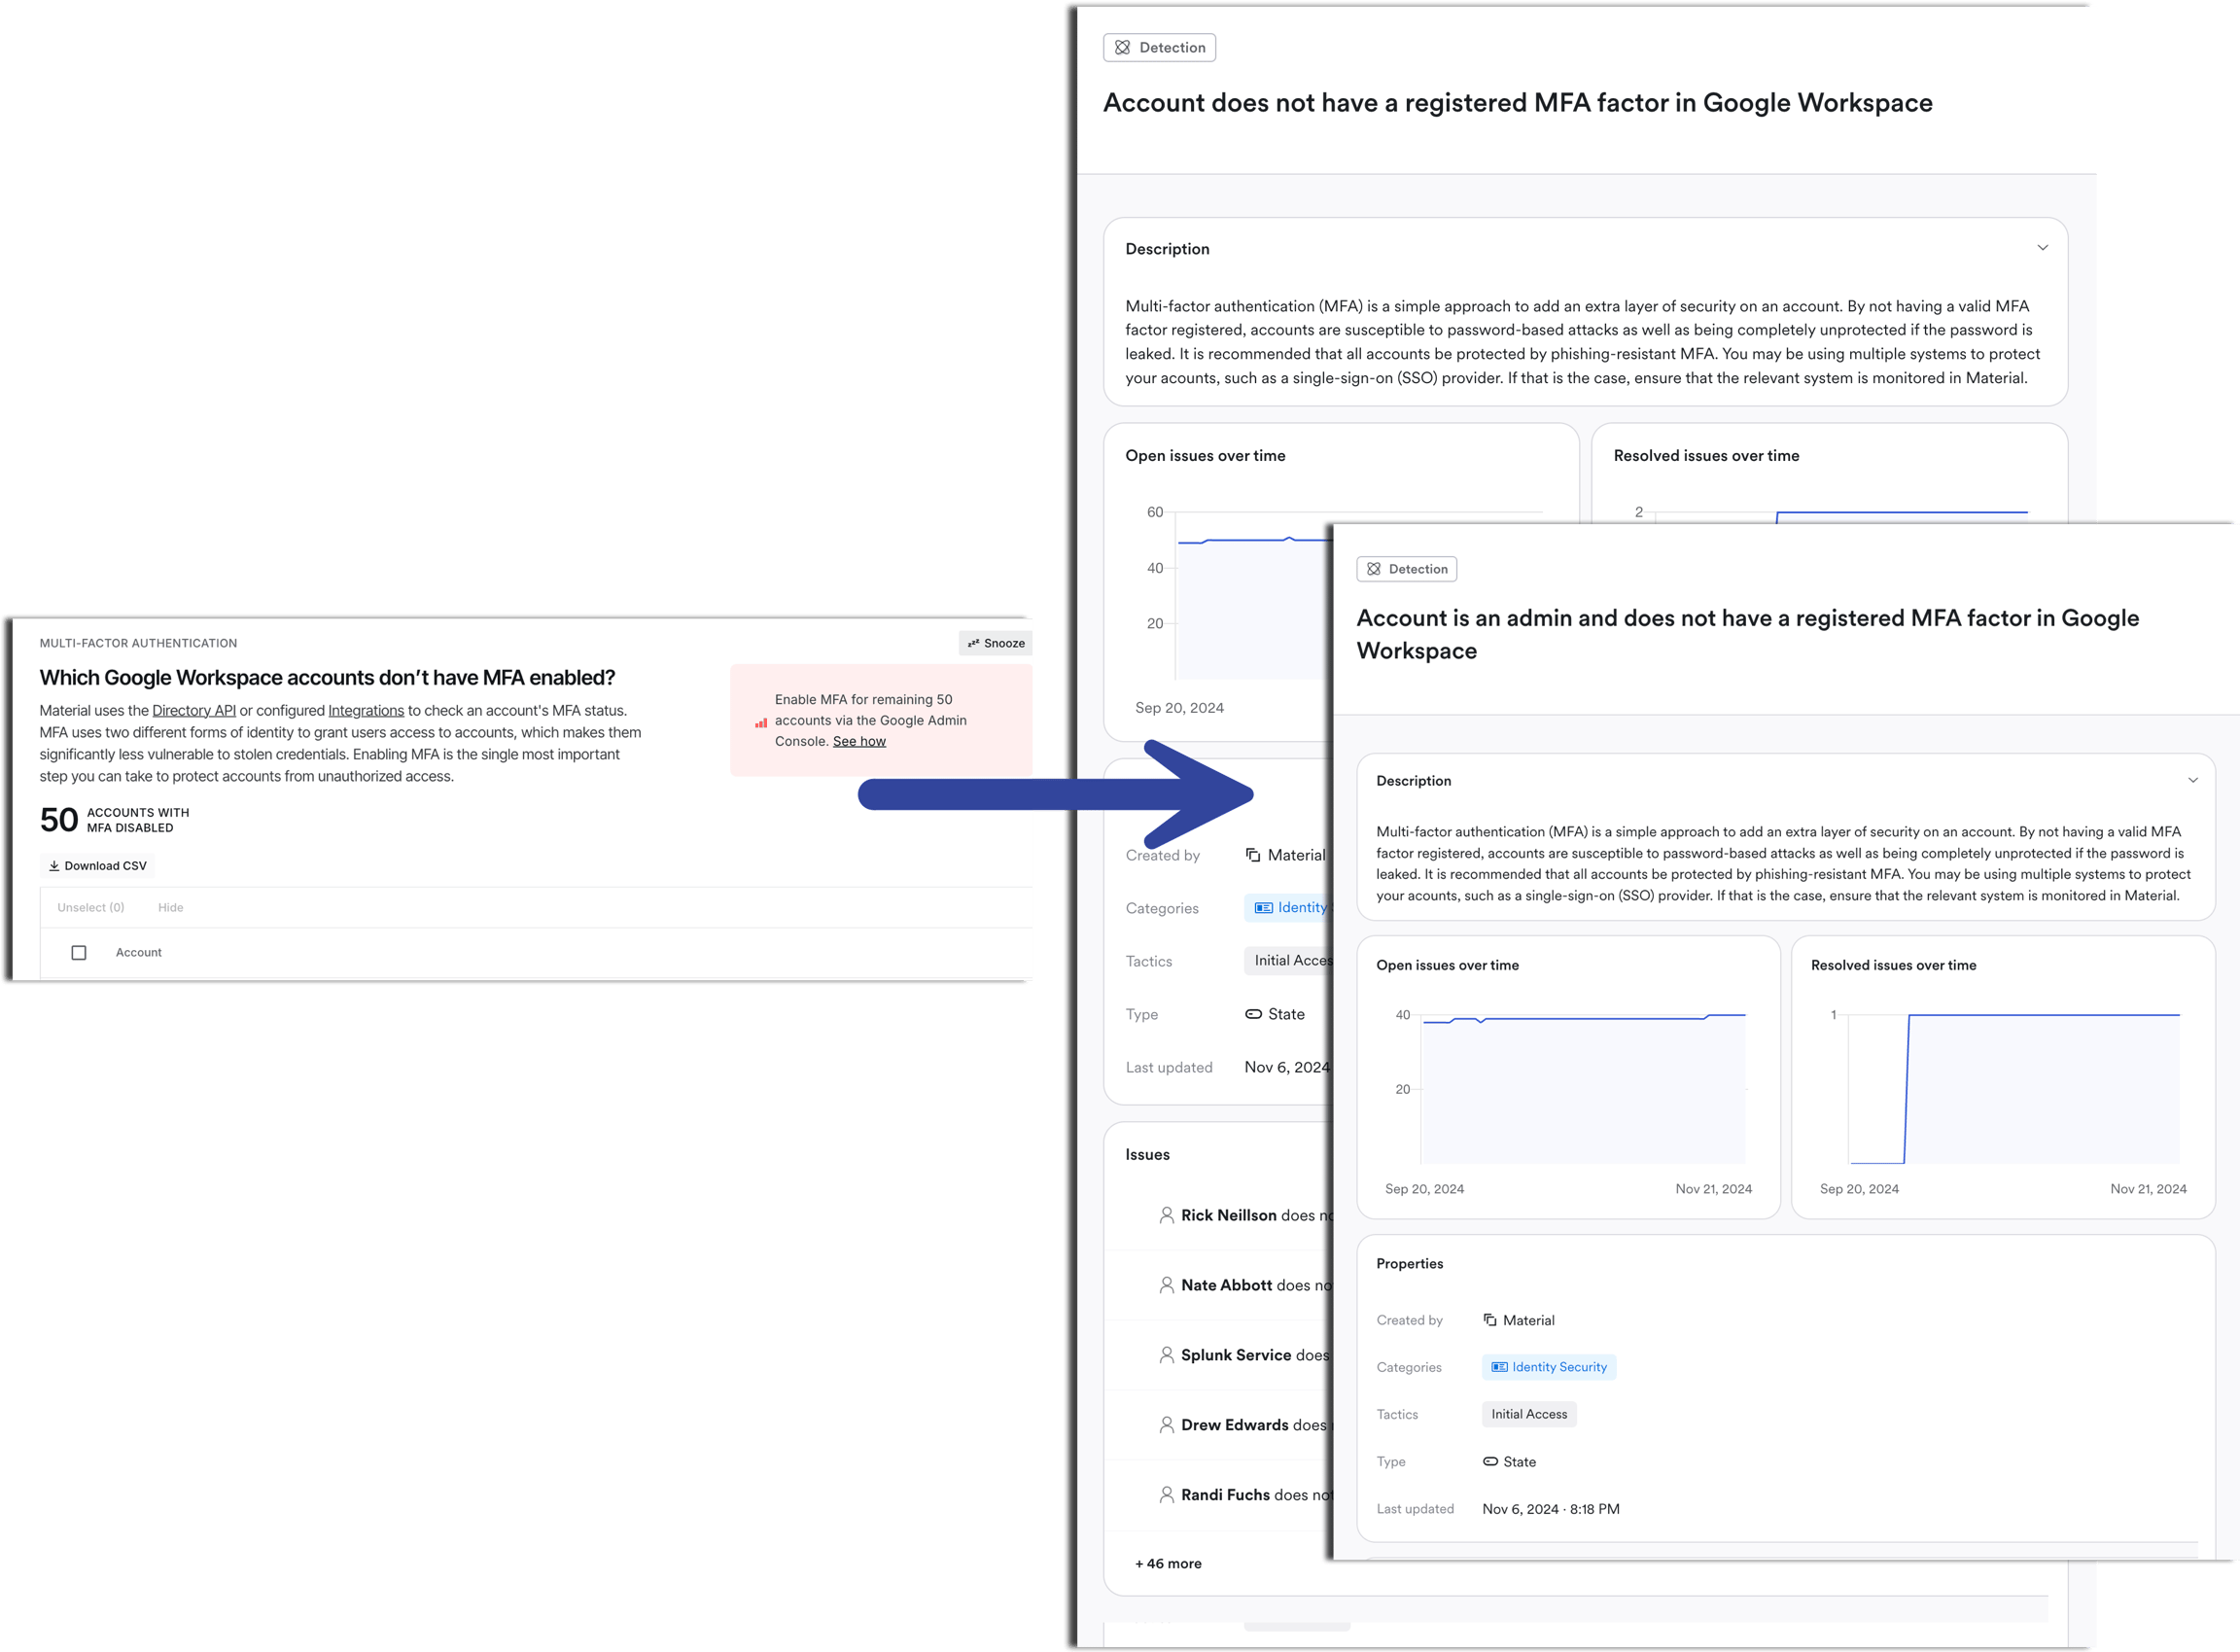
Use these tables to find the detections that the data in previous Posture Management reports are now located in.
Data Breaches
Which accounts are part of public data breaches?
Account is present in a known data breach
Which apps used in my organization were part of public data breaches?
Issues created by the detection "Account is present in a known data breach" include app information as evidence
Which partners were part of public data breaches?
This report has been sunset.
Groups
Which Google Groups allow external users to post messages?
Google group with VIP members has weak moderation settings and allows external senders to post
Google group has weak moderation settings and allows external senders to post
Google group allows external senders to post
Google group allows external members
Mail Forwarding
Which Google accounts are using auto-forwarding?
Which Microsoft 365 accounts are using auto-forwarding?
Which accounts forward work email to personal accounts?
Account forwarded a sensitive email to a personal account
Account automatically forwards all emails externally
Account automatically forwards all emails to a freemail domain
Account automatically forwards a subset of emails externally
Account automatically forwards a subset of emails to a freemail domain
Account forwarded an email to a personal account
Account automatically forwards all emails internally
Account automatically forwards a subset of emails internally
Multi-Factor Authentication (MFA)
Which Google Workspace accounts don’t have MFA enabled?
Google account does not enforce MFA
Which Microsoft 365 accounts don’t have MFA enabled?
Microsoft Account used a non-phishing-resistant MFA factor to log in
Account does not have a registered MFA factor in Microsoft 365
Account has a non-phishing-resistant MFA factor registered in Microsoft 365
Which Google accounts have MFA bypasses?
Google account syncing using IMAP/POP
Google account is using application-specific passwords
Partners
Which partners have the most sensitive content?
None. Relocated to Reports->Sensitive Content as "Where was sensitive content sent?"
Which partners were part of public data breaches?
Account is present in a known data breach
Sensitive Content
What unprotected sensitive content exists in mailboxes?
None. Relocated to Reports->Sensitive Content.
Which partners have the most sensitive content?
None. Relocated to Reports->Sensitive Content.
Third-party Apps
Which apps have OAuth access to Google accounts?
None. Relocated to Reports->Apps.
Which apps are used in my organization?
None. Relocated to Explorer->Apps.
Which apps perform unprotected account access requests over email?
None. Relocated to Reports->Apps.
Which apps used in my organization were part of public data breaches?
Account is present in a known data breach
View Material Detections for All Categories
You can now view all Material Detections in one list, sort and filter that list, view descriptions, related issues, and more — all in once place. Learn more here.
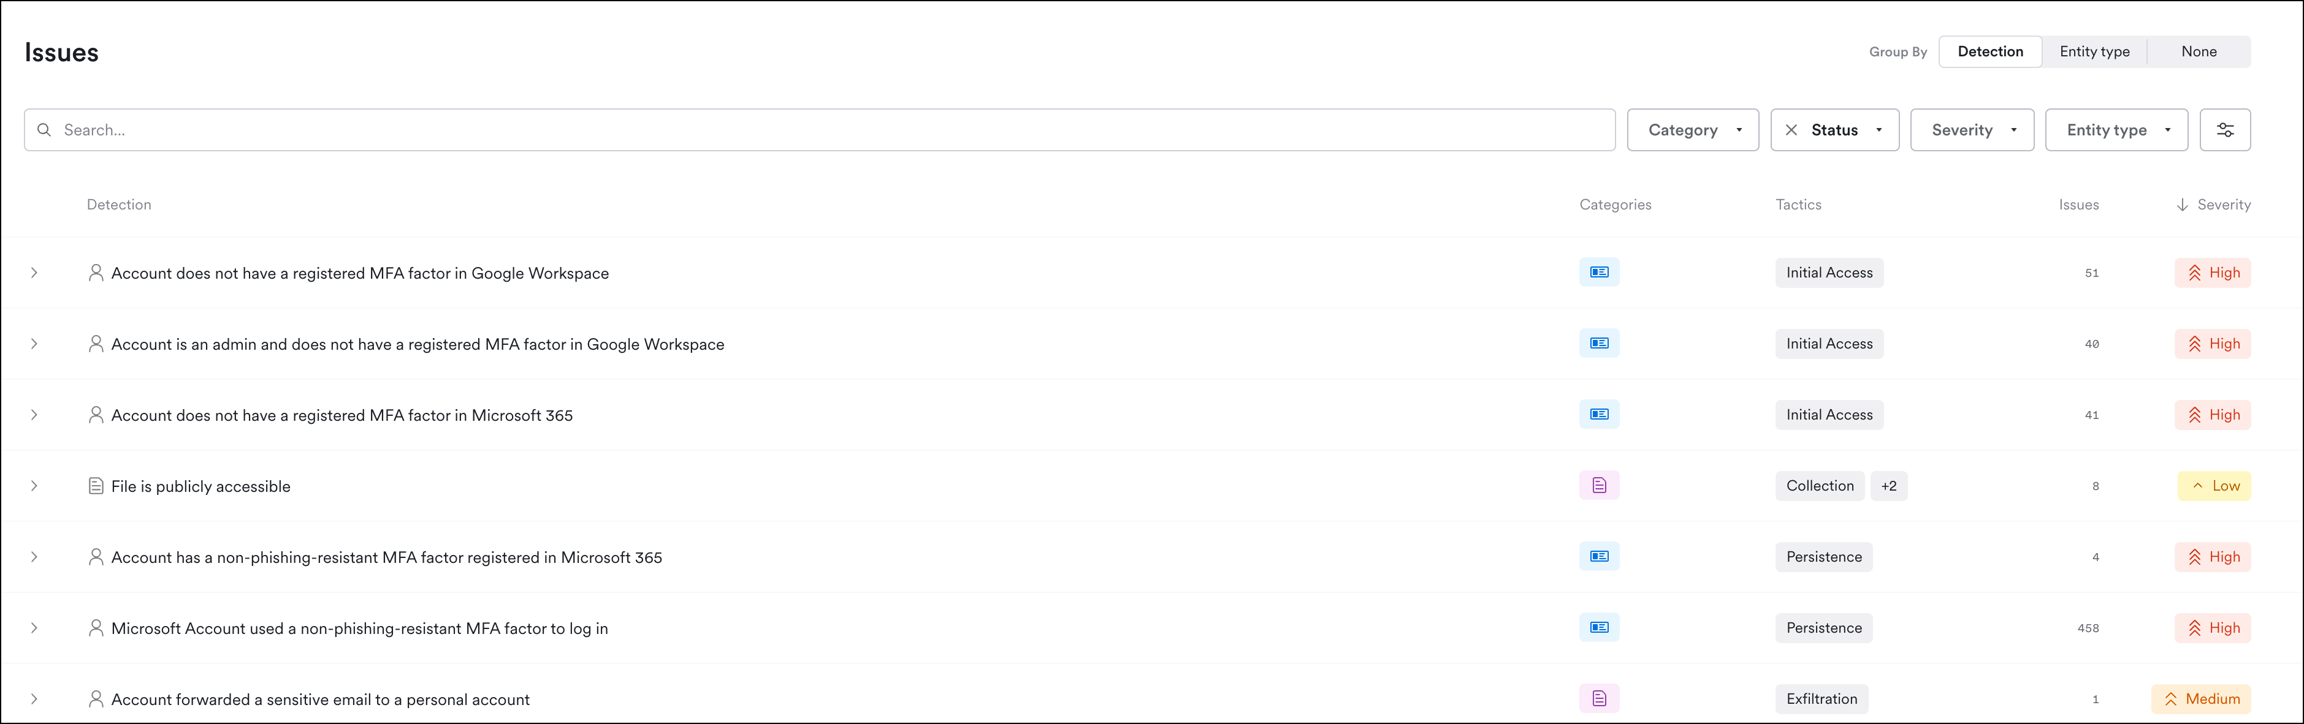
You can also configure default remediation and response directly from the detection. Learn more here.
Permissions Updates
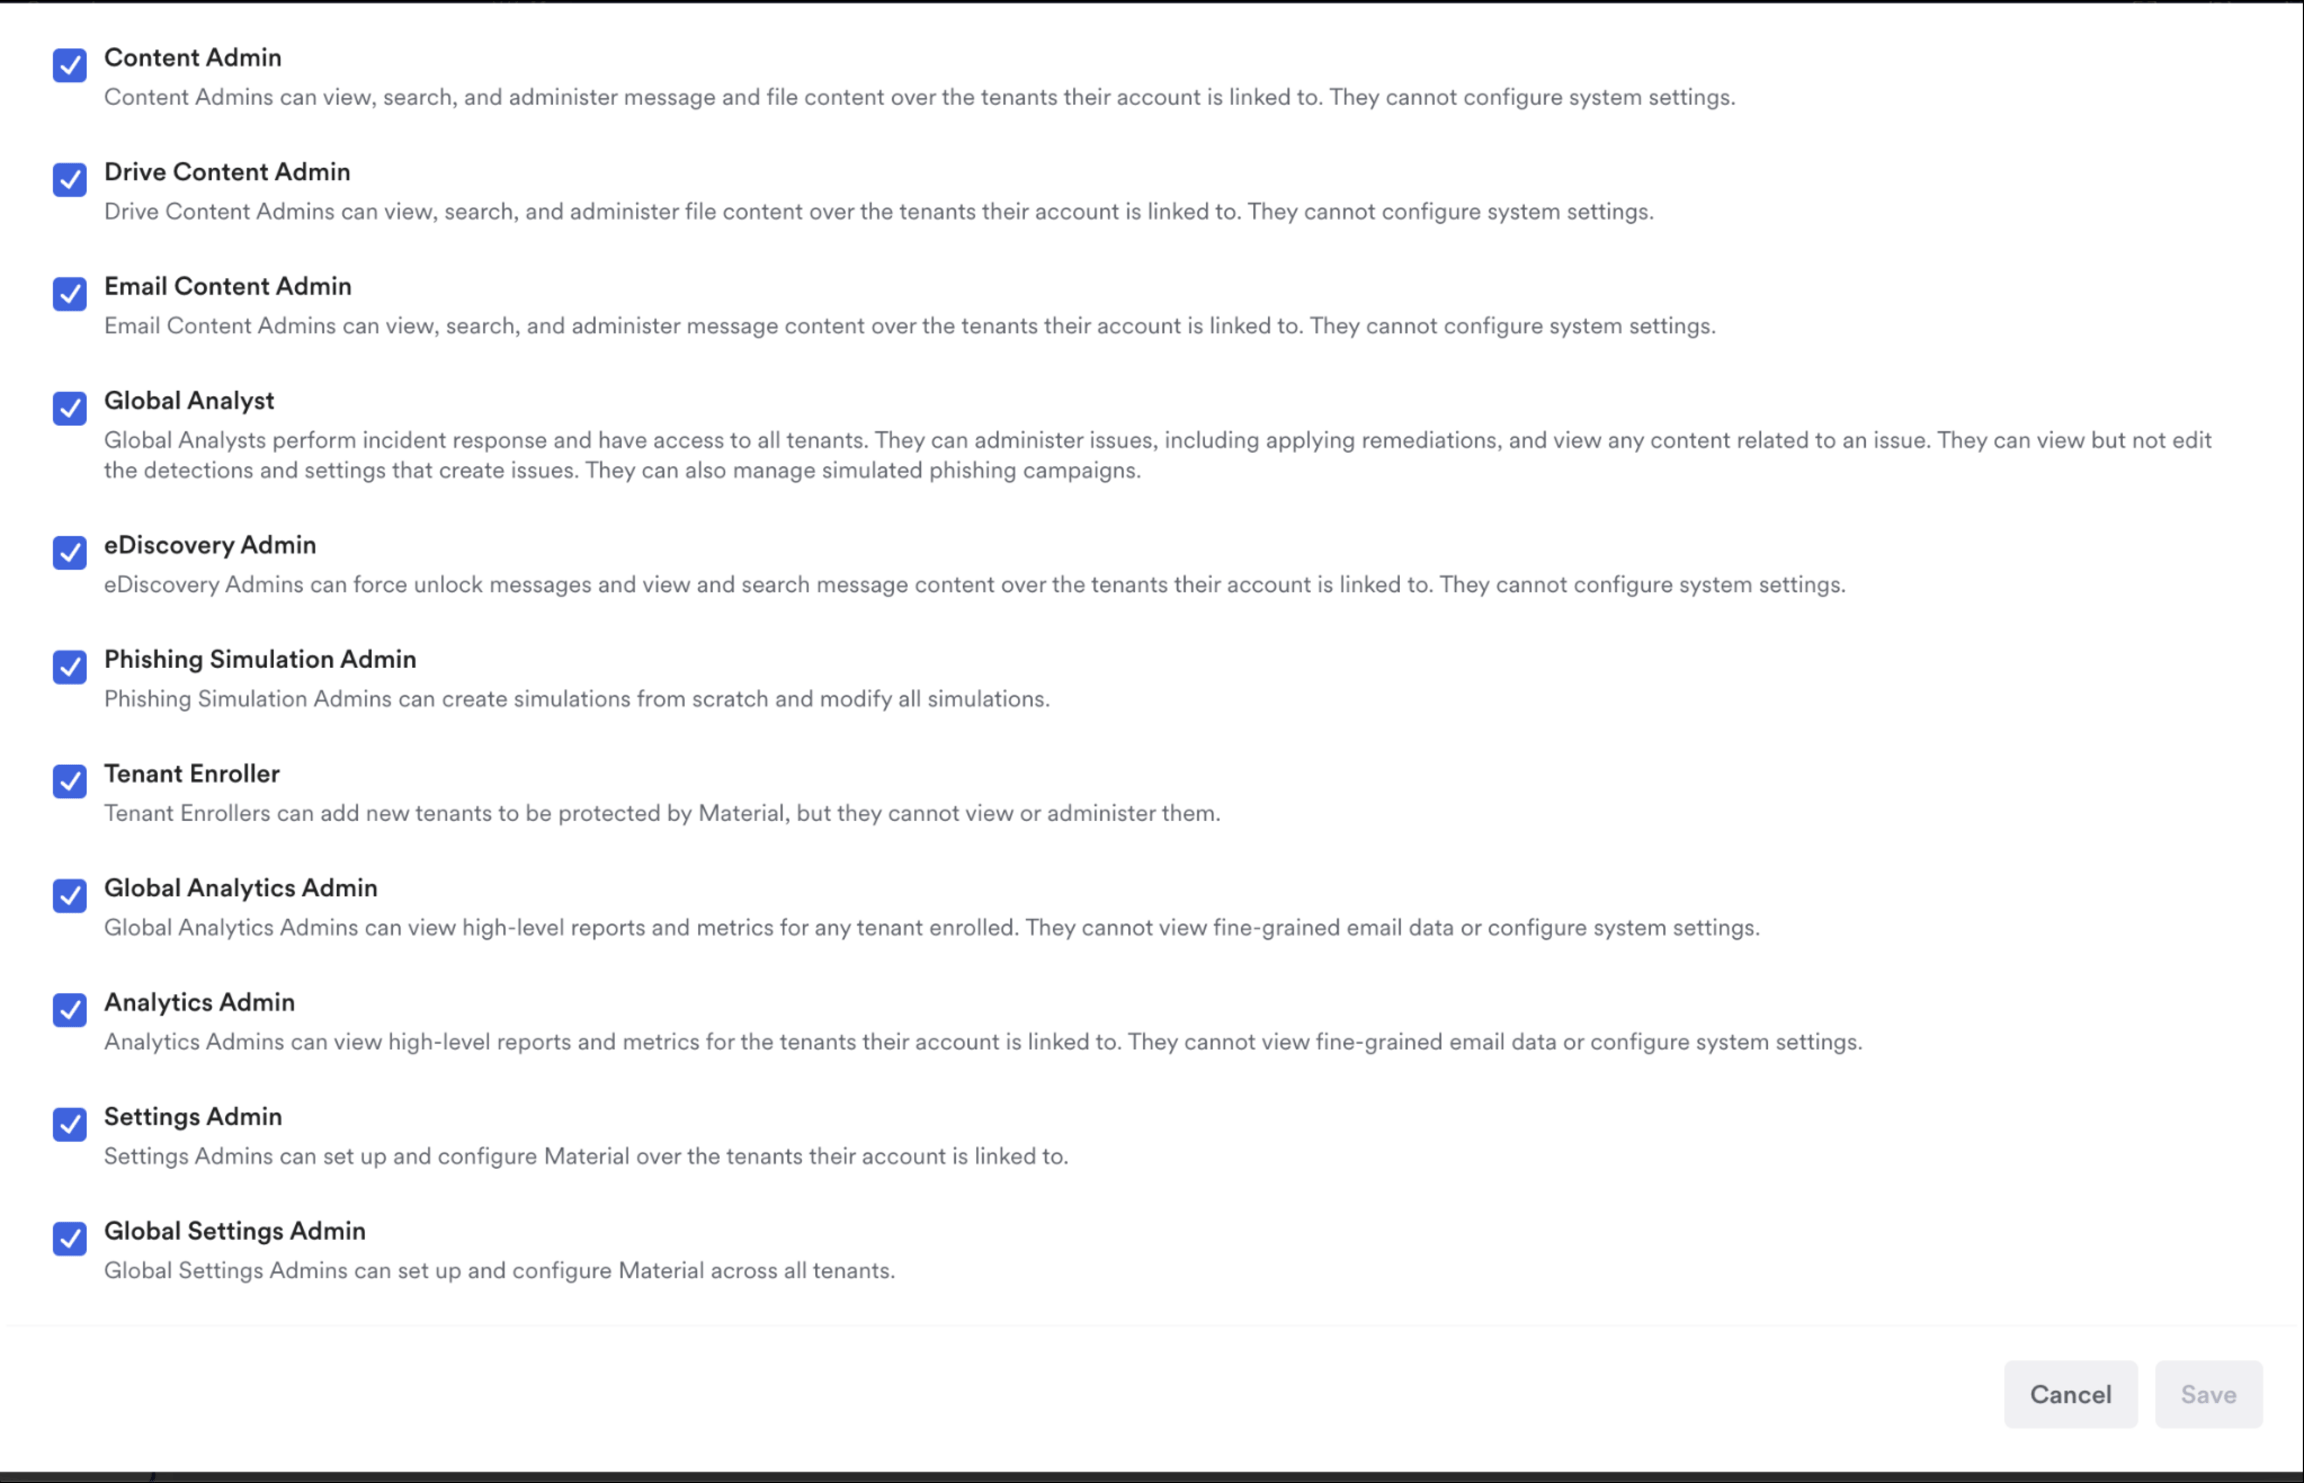
We made some updates to our roles and permissions:
Triage Admin is now Global Analyst.
This role can see all issue types and the associated metadata and content directly tied with the issue across all tenants (e.g. flagged message or file contents)
To search, users need the Content Admin role
File Data Protection New Location
File Data protection is now included in Material Detections and behaves the same as it did previously.
To view File-related Detections:
From the left navigation, click Detections.
Click Filters, then Entity Type, then select File.
To view File-related Issues:
From the left navigation, click Issues.
Click Filters, then Entity Type, then select File.
Email Data Protection New Location
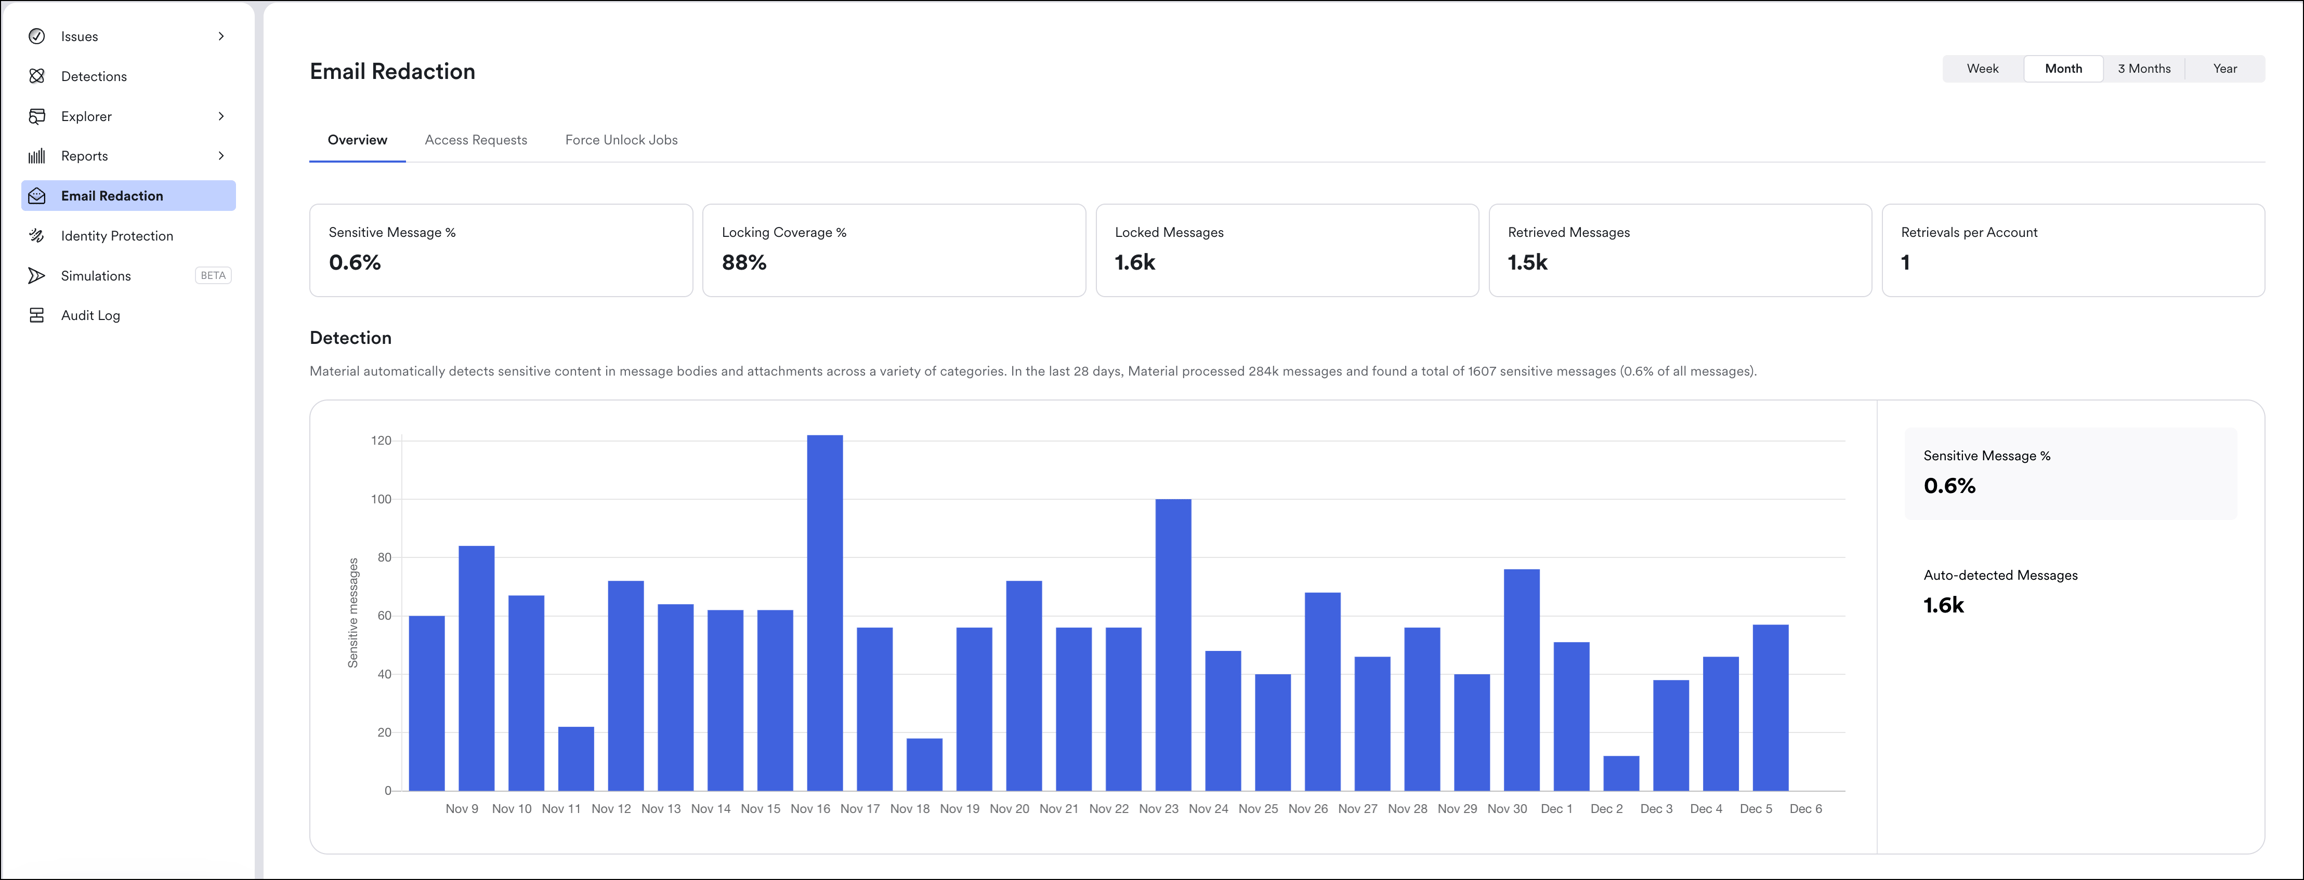
To view your Dashboards, Access Requests, and Force Unlock jobs:
From the left navigation, click Email Redaction.
Click Email Redaction:
Email Threats New Location
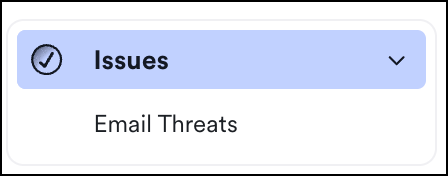
Email Threats (formerly Phishing Protection) are now nested under Issues:
Accounts New Location
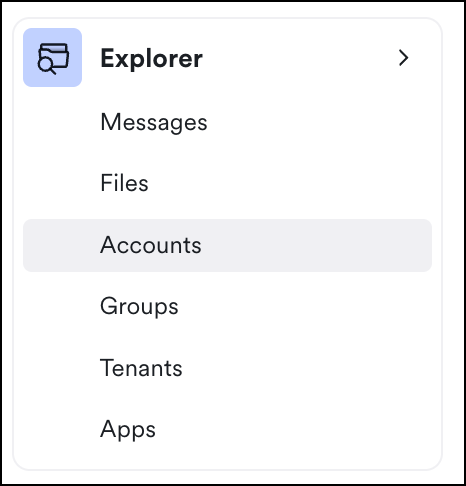
Accounts are now located in the Explorer:
Give Feedback
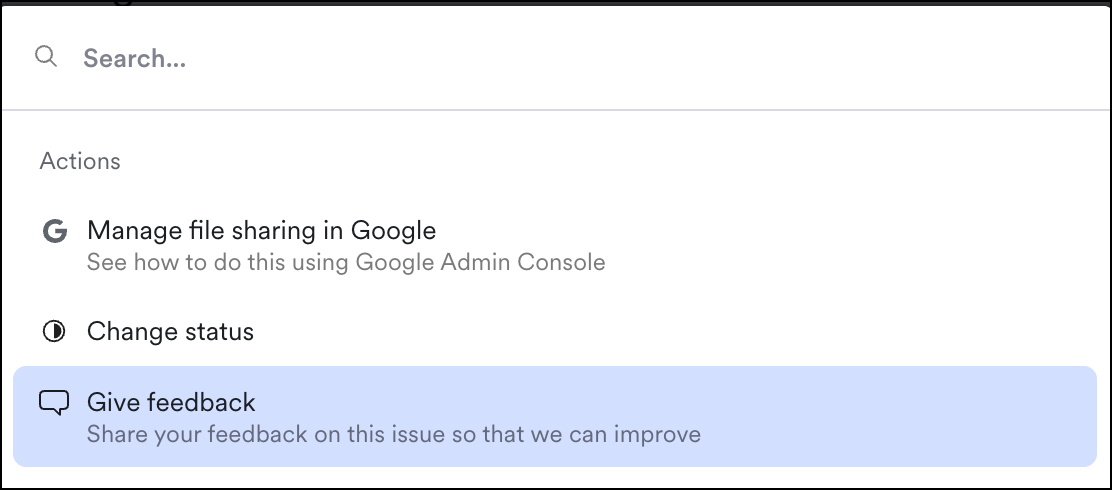
Share your experience with or feedback about an issue or detection!
Open any Detection or Issue.
Press
⌘Kto open Spotlight.Choose Give Feedback to send comments directly to our Product team.
Last updated
Was this helpful?