

Email Identity Protection
Manage email-based app access
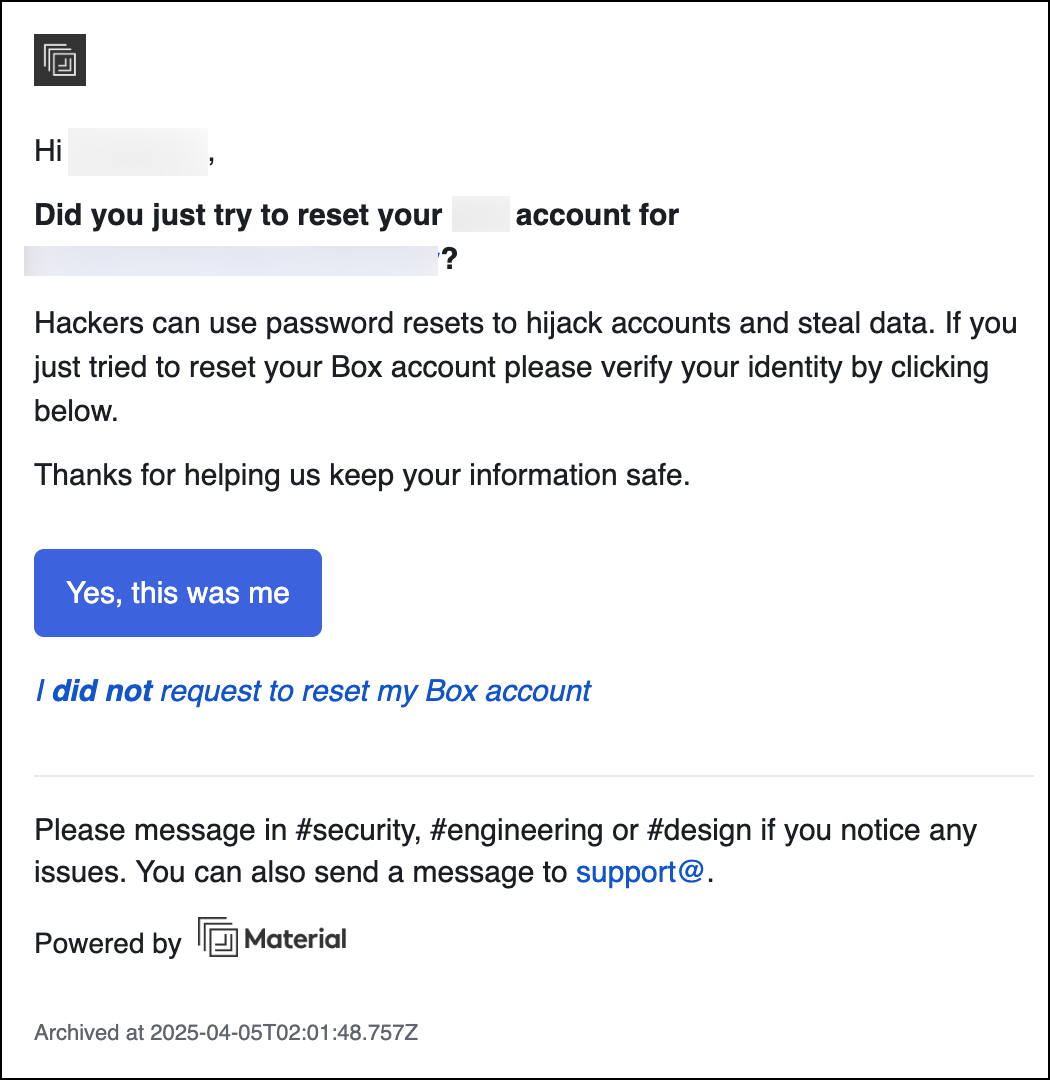
Email Identity Protection adds an authentication step before allowing users to access password resets and other types of account verification messages. This prevents attackers from using compromised mailboxes to hijack other services.
About Email Identity Protection
If an attacker gains access to a user’s mailbox, they will often attempt to use it as an entry point to additional services, identifying target applications based on communication received by the user. Applications that use email as a mechanism for identity verification for account maintenance workflows (e.g. password resets, signup confirmations, etc.) are especially vulnerable to this type of attack.
Email Identity Protection provides protection against this type of attack by automatically identifying and protecting account maintenance messages from the most common business applications. The protection works by intercepting messages and only delivering them after the end user completes an additional verification step (e.g., Okta Verify Request).
This protection can be enabled wall-to-wall or for a subset of accounts or groups.
Using Server-Side Routing
Email Identity Protection can be used with or without Server-Side Routing. We highly recommend enabling this feature, as it ensures that account maintenance messages will always be intercepted before they are delivered to user mailboxes. Learn more in the ATO Deployment Guide.
FAQs
How are target messages intercepted?
With Server-Side Routing: Material uses Mail Flow Rules in Microsoft 365 and Content Compliance Rules in Google Workspace to identify and reroute messages to a buffer account. No MX record changes are required.
Without Server-Side Routing: Material monitors new messages as they are delivered and protects them promptly after delivery.
Where are protected messages stored while verification is pending?
Messages are stored in a storage bucket inside your private, dedicated Material cloud instance. When a user retrieves a message or if Email Identity Protection is disabled for a user, messages are returned to the mailbox in their original form.
Can Email Identity Protection be disabled after-the-fact?
Yes, you can disable Email Identity Protection at any time, which will prevent future messages from being intercepted. Previously intercepted messages that were not verified by users will not be restored.
Last updated
Was this helpful?