

Custom Detections
Material Detections are designed and updated constantly to be effective in identifying threats. You can also define your own criteria using Custom Detections if there's a specific use case you want to detect that is not covered by the Material Detections.
You create and edit a custom detection in a single editor, where you set the matching criteria, choose the classification matches receive, and configure the response before you save.
Create a Custom Detection
From the Detections page, click Create Detection.
Choose a detection type: file or message.
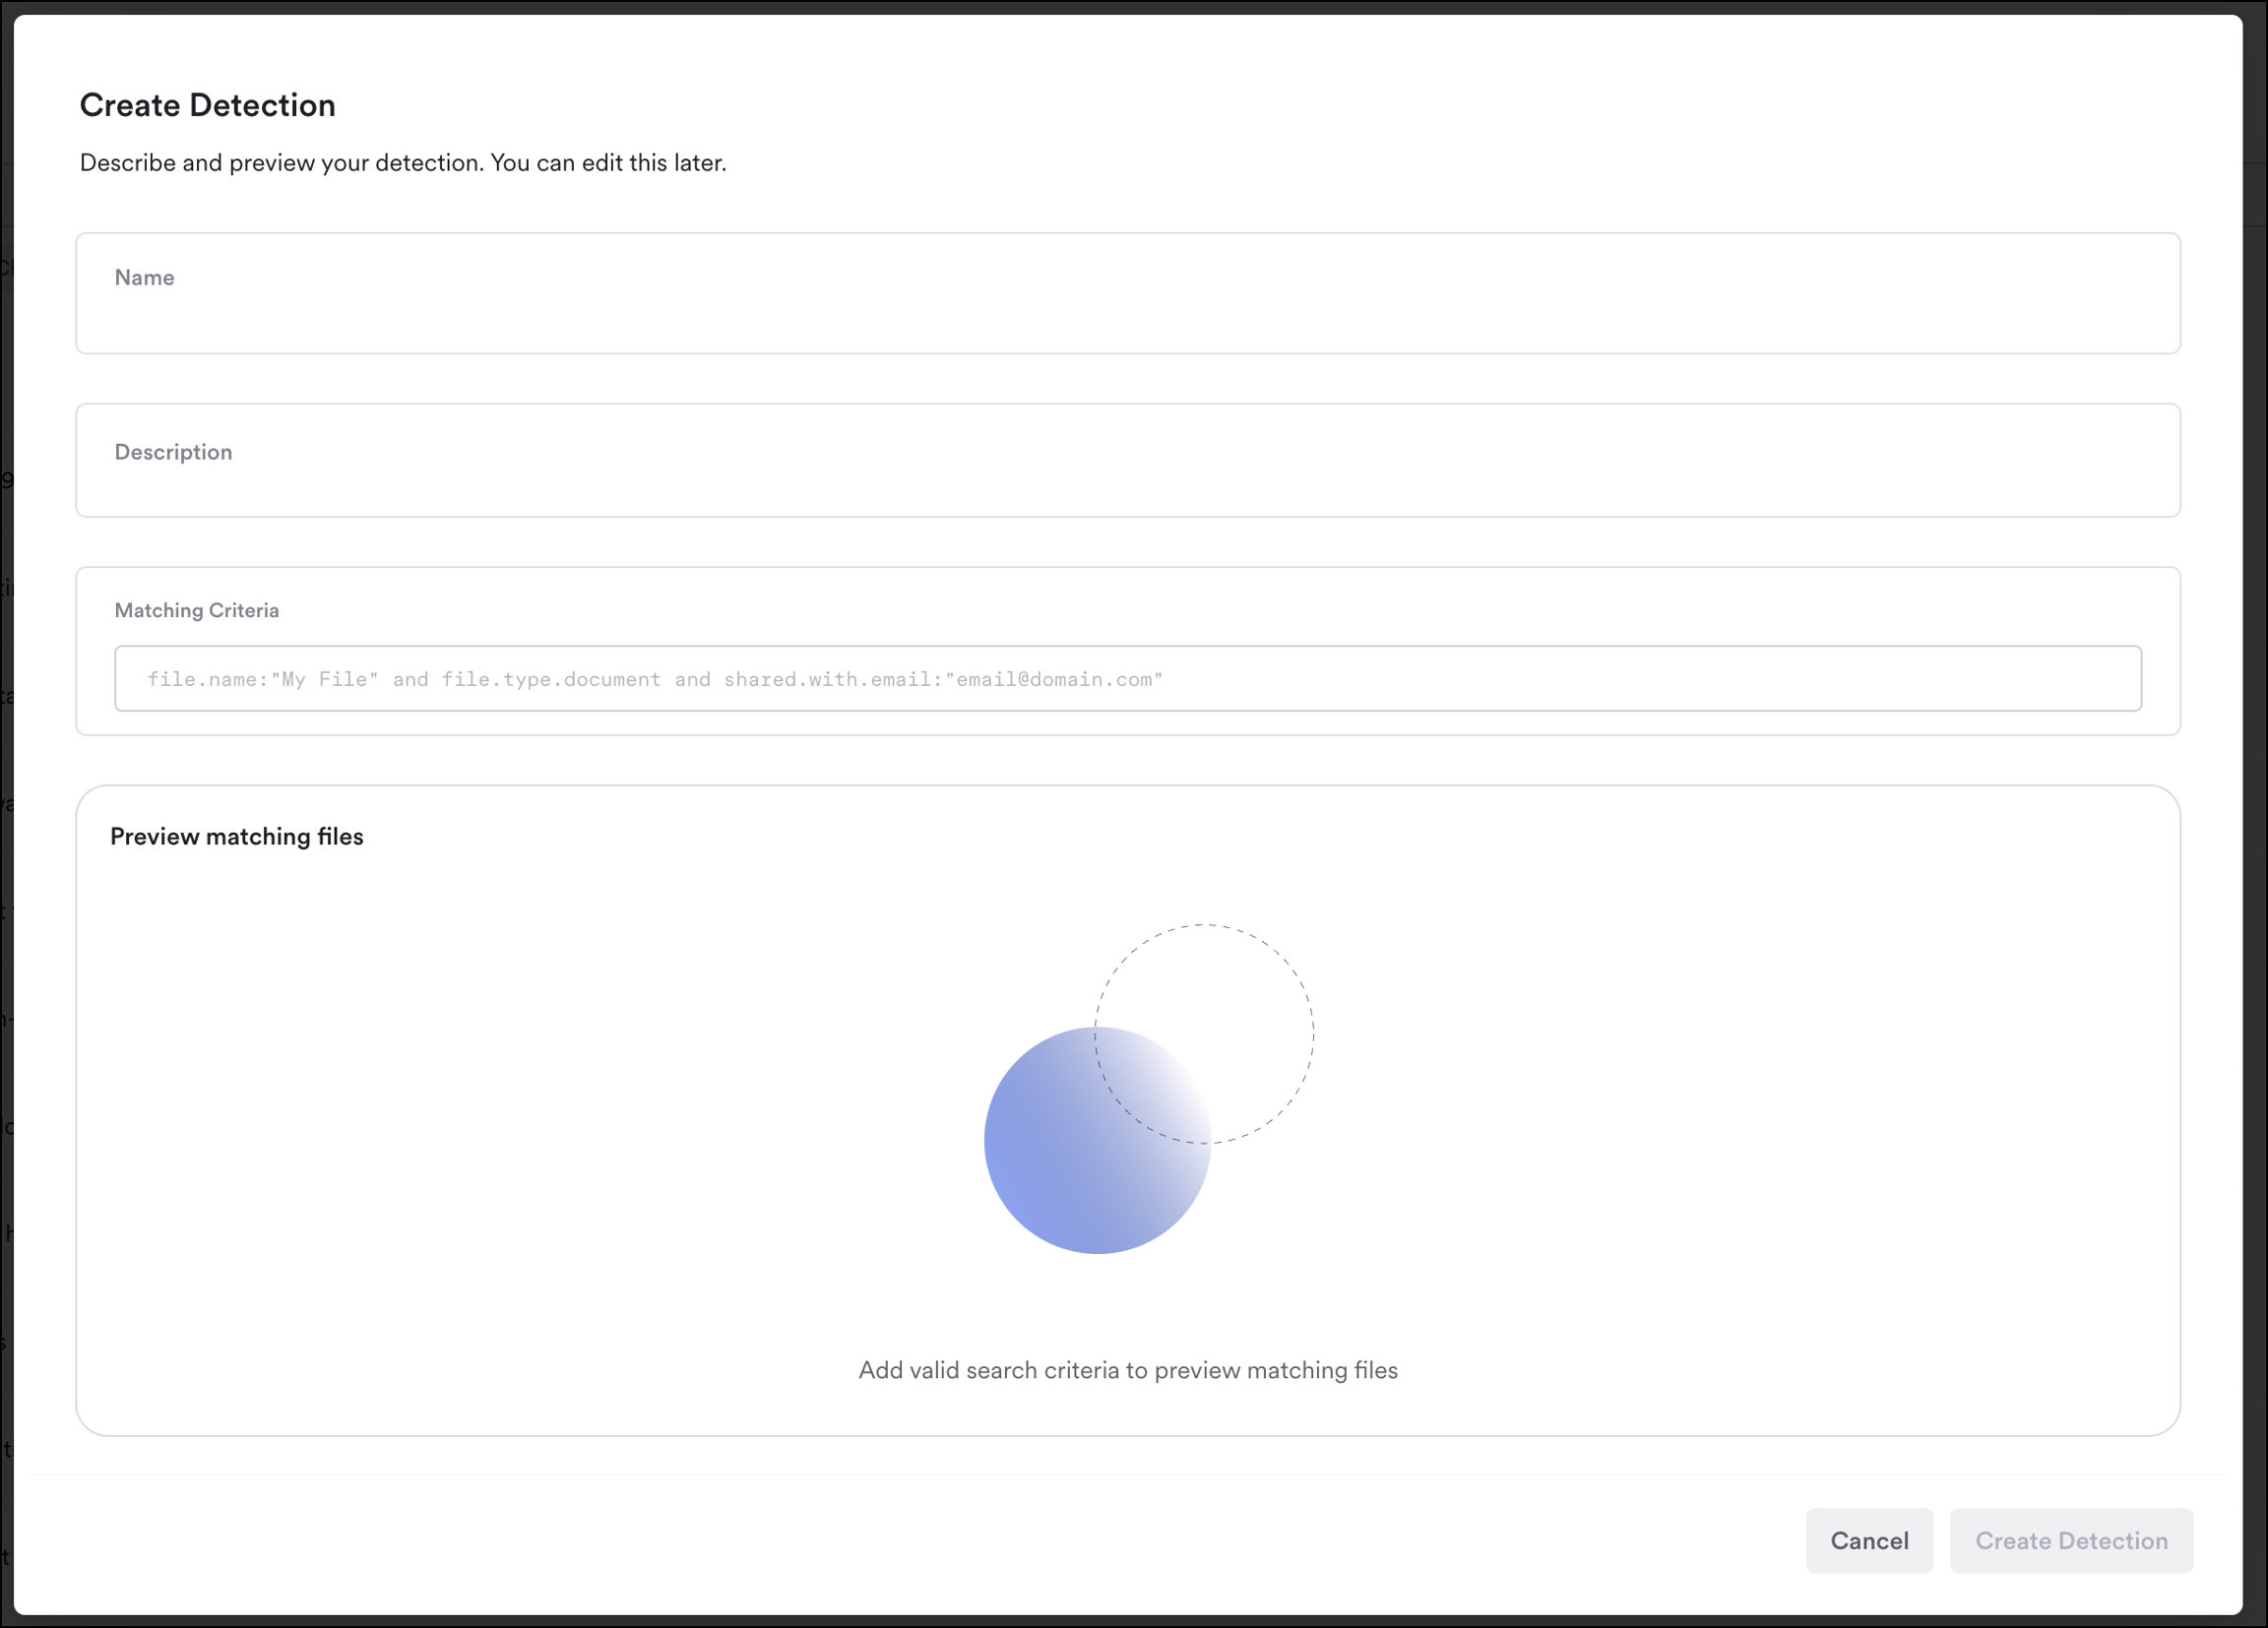
Custom Detection Screen Complete the Matching Criteria with the logic you want this to detect.
Name and describe your detection. Consider aligning your naming structure with Material's (entity: issue, for example Account doesn't have MFA enabled).
For Message detections, choose the classification that matching messages or files receive: Safe, Malicious, Spam, or Unknown. Use Unknown to signify a message you want to review without asserting a particular verdict.
Configure the response for matches.
Preview matching files or messages.
Click Create Detection and the detection will appear in your detection list. Message detections are enabled by default; file detections must be explicitly enabled. The detection author appears in the Created By property.
Newly created message detections may take up to 5 minutes to take effect.
How overlapping detections are handled
If multiple detections match a message, only one issue is created, and the issue appears under only one Detection. In the issue you can see a list of all detections that matched.
The strictest set of remediations from all the detections that matched (regardless of whether they are Material Detections or Custom Detections) is applied to each messages.
An issue is created for each file detection that matches a file, even if there is more than one detection that matches.
Edit a Custom Detection
Open the detection from the Detections page to edit it in the same editor used to create it. Make your changes, then save. Changes to message detections may take up to 5 minutes to take effect.
Archive a Custom Detection
From the Detections page, open the detection then click Archive. Archiving disables the detection, hides it from the list, and offers to update any open issues it created. To re-enable an archived detection, unarchive it first from the detection details view.
To view archived detections on the Detections page, deselect Hide Archived from the filter list.
Last updated
Was this helpful?